
Explore our insights on IT solutions and business growth.
Discover valuable information and stay informed on the latest industry developments.
Managed IT Services for Biotech Startups: What to Expect Before You Scale
Preparing to scale? Biotech startups need robust IT compliance, IAM, and immutable backups before their next funding round. Learn how to secure your data here.
IT Growing Pains Post-Series A: The Blind Spots Between Rounds
Managing IT growing pains after Series A? Here’s how Bay Area startups solve access drift, tool sprawl, and compliance gaps before the next diligence team finds them.
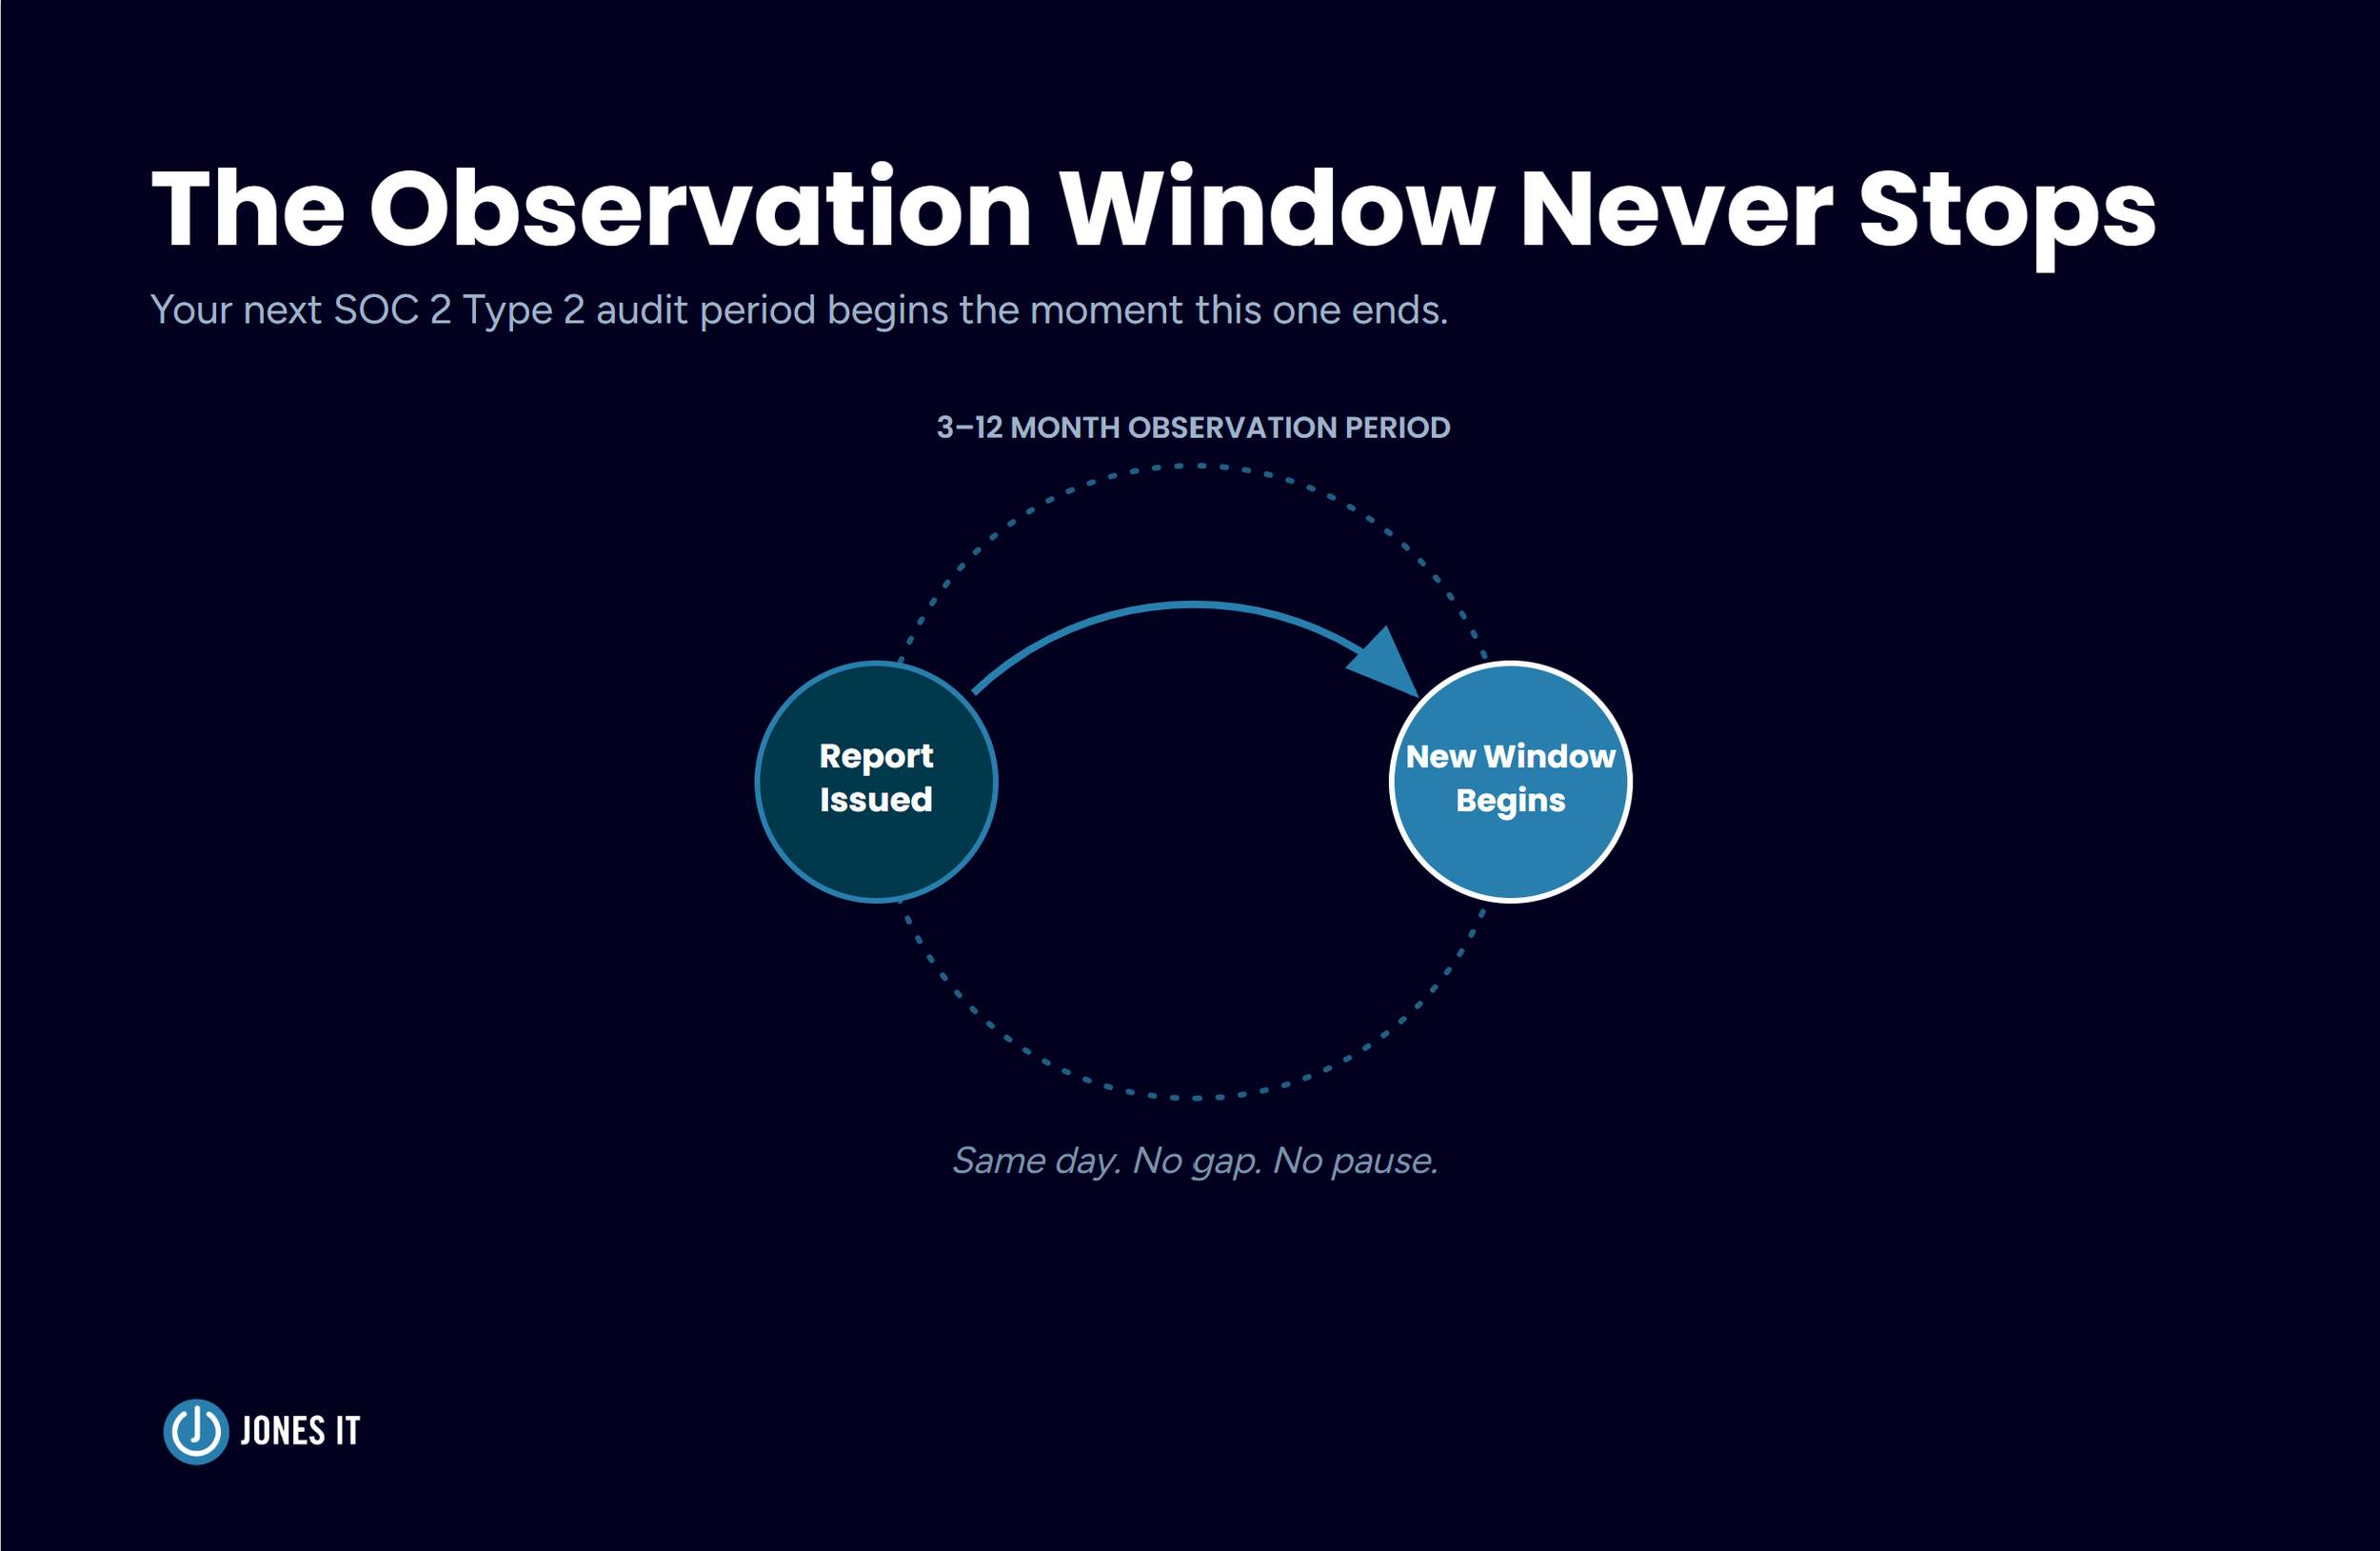
Maintaining SOC 2 Compliance: How to Avoid the Post-Audit Gap
Wondering how to maintain SOC 2 compliance after your first audit? Learn the essential year-one cadence, avoid the "Q3 Gap," and keep your certification stress-free.
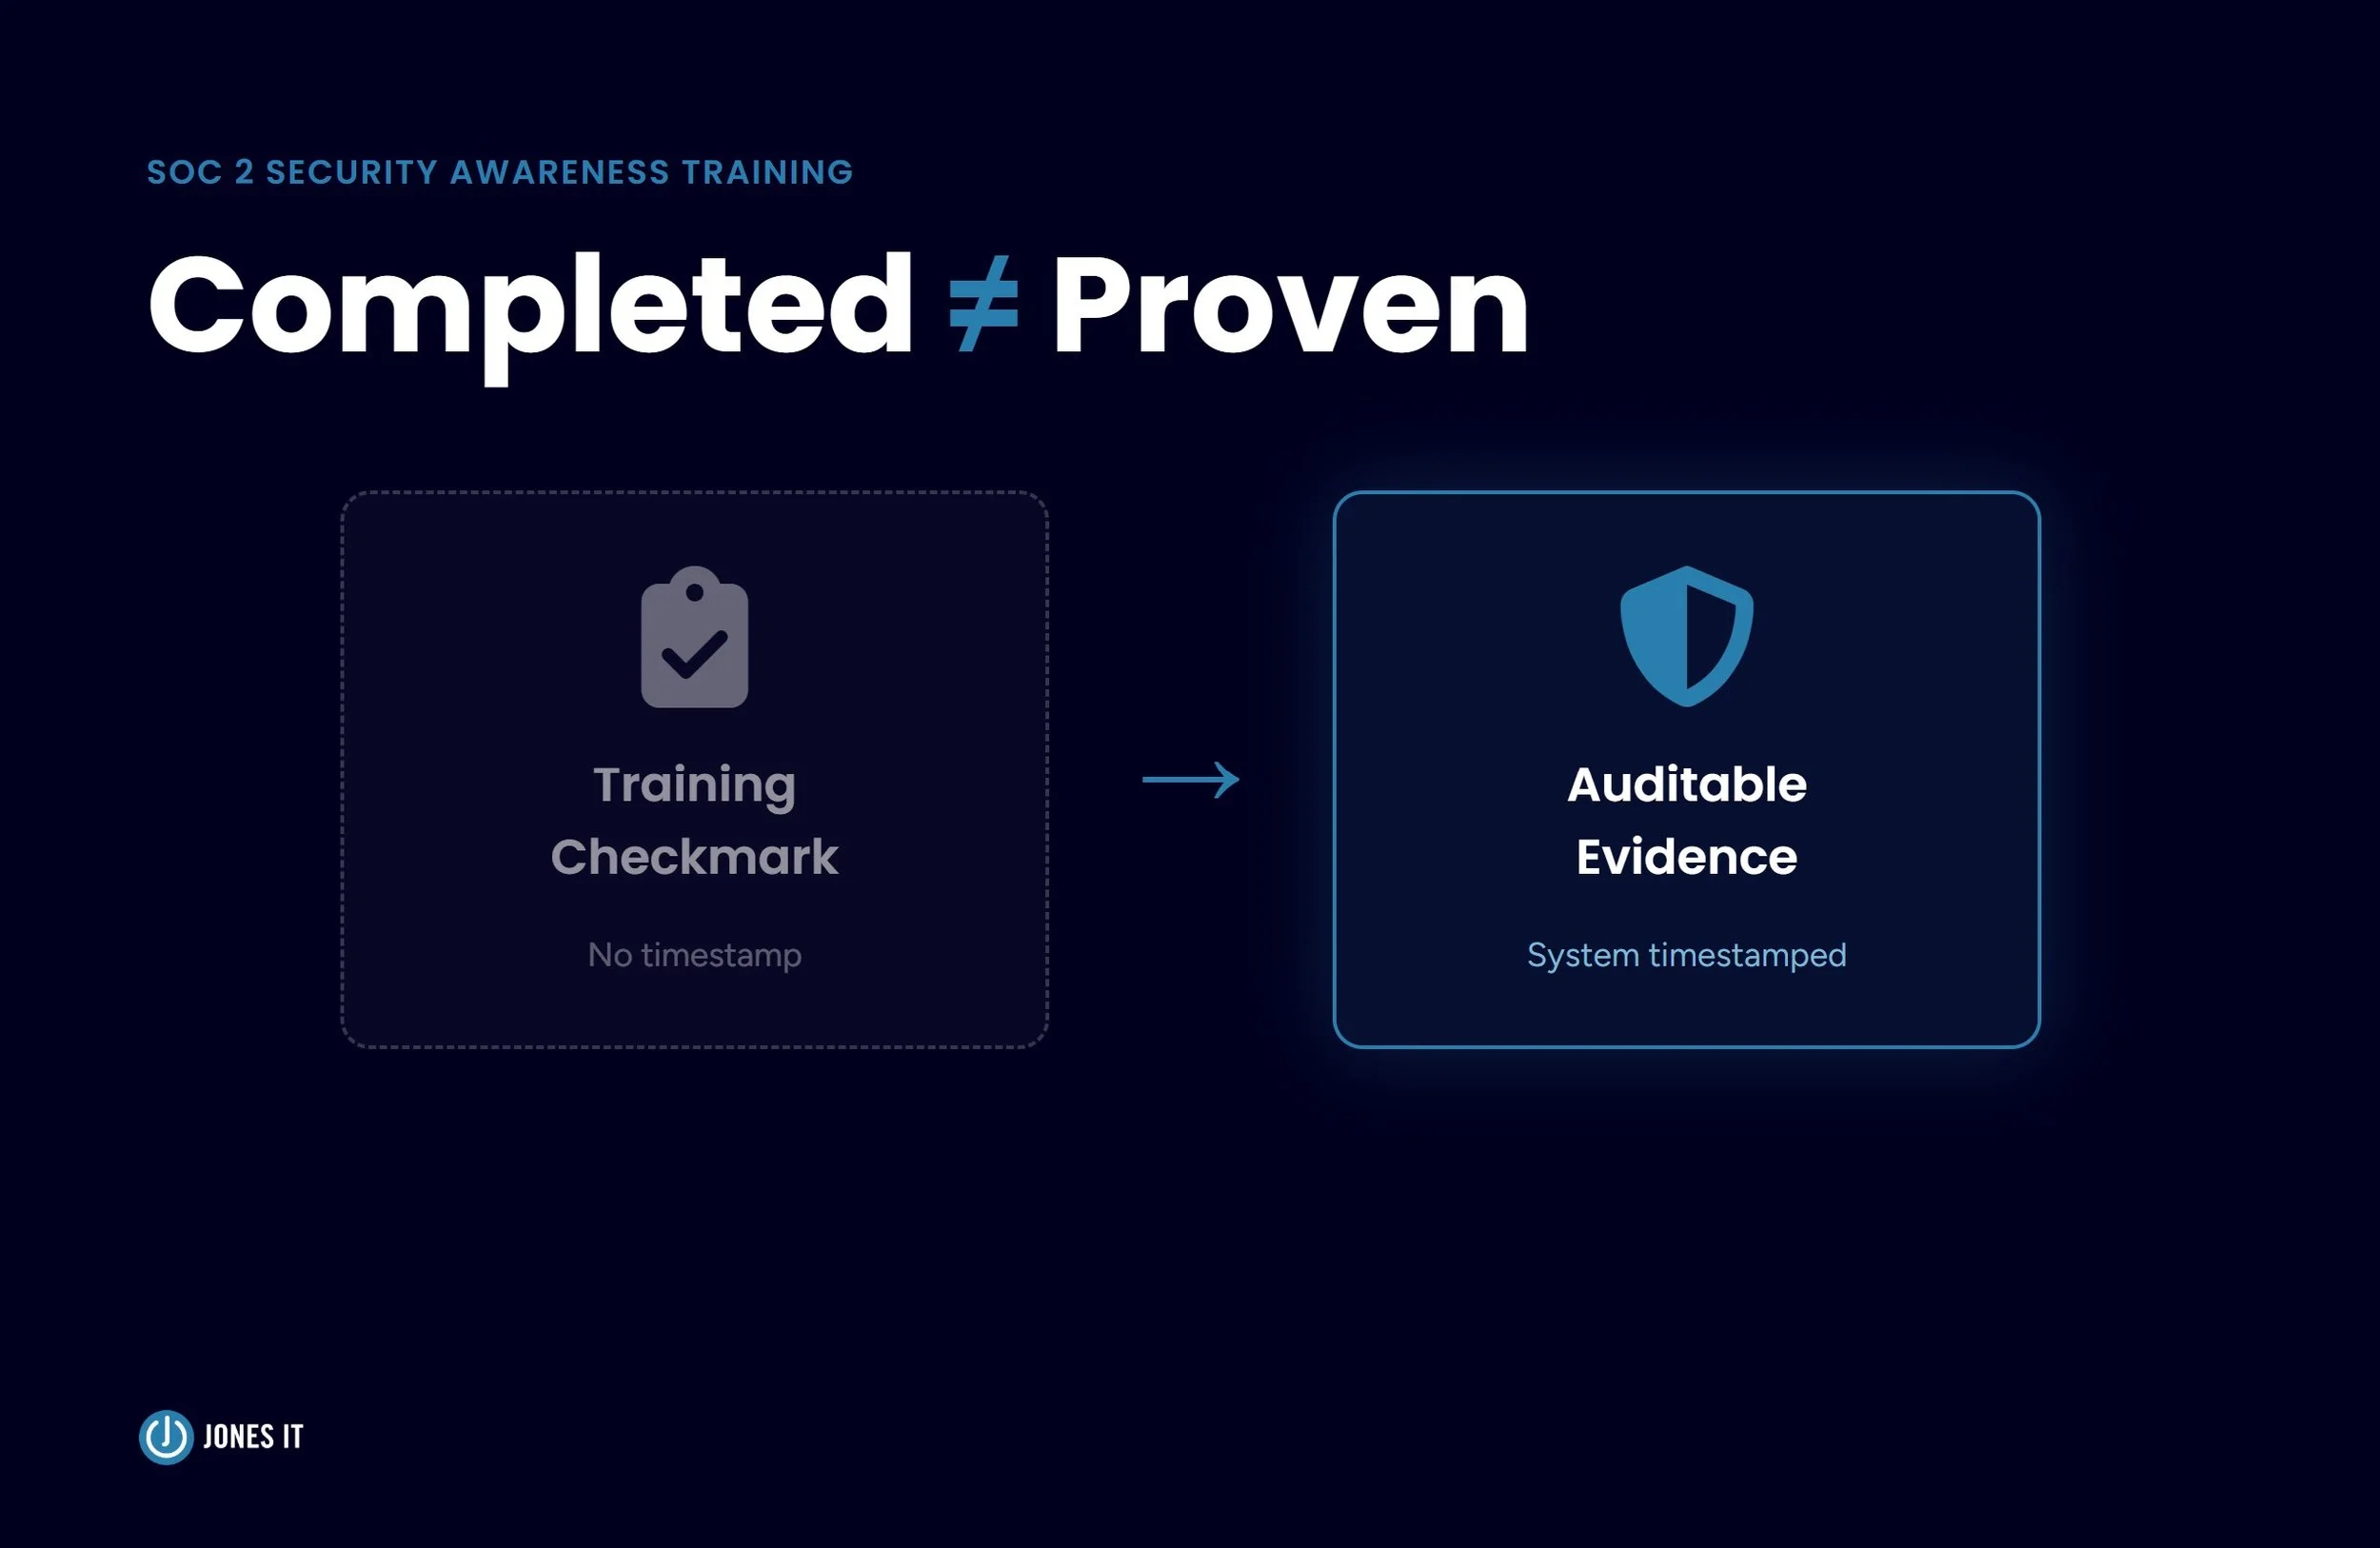
SOC 2 Security Awareness Training: What Your Auditor Actually Wants to See
Your team can complete security training and still fail a SOC 2 control. Learn the five evidence artifacts auditors require and how to close the gap.
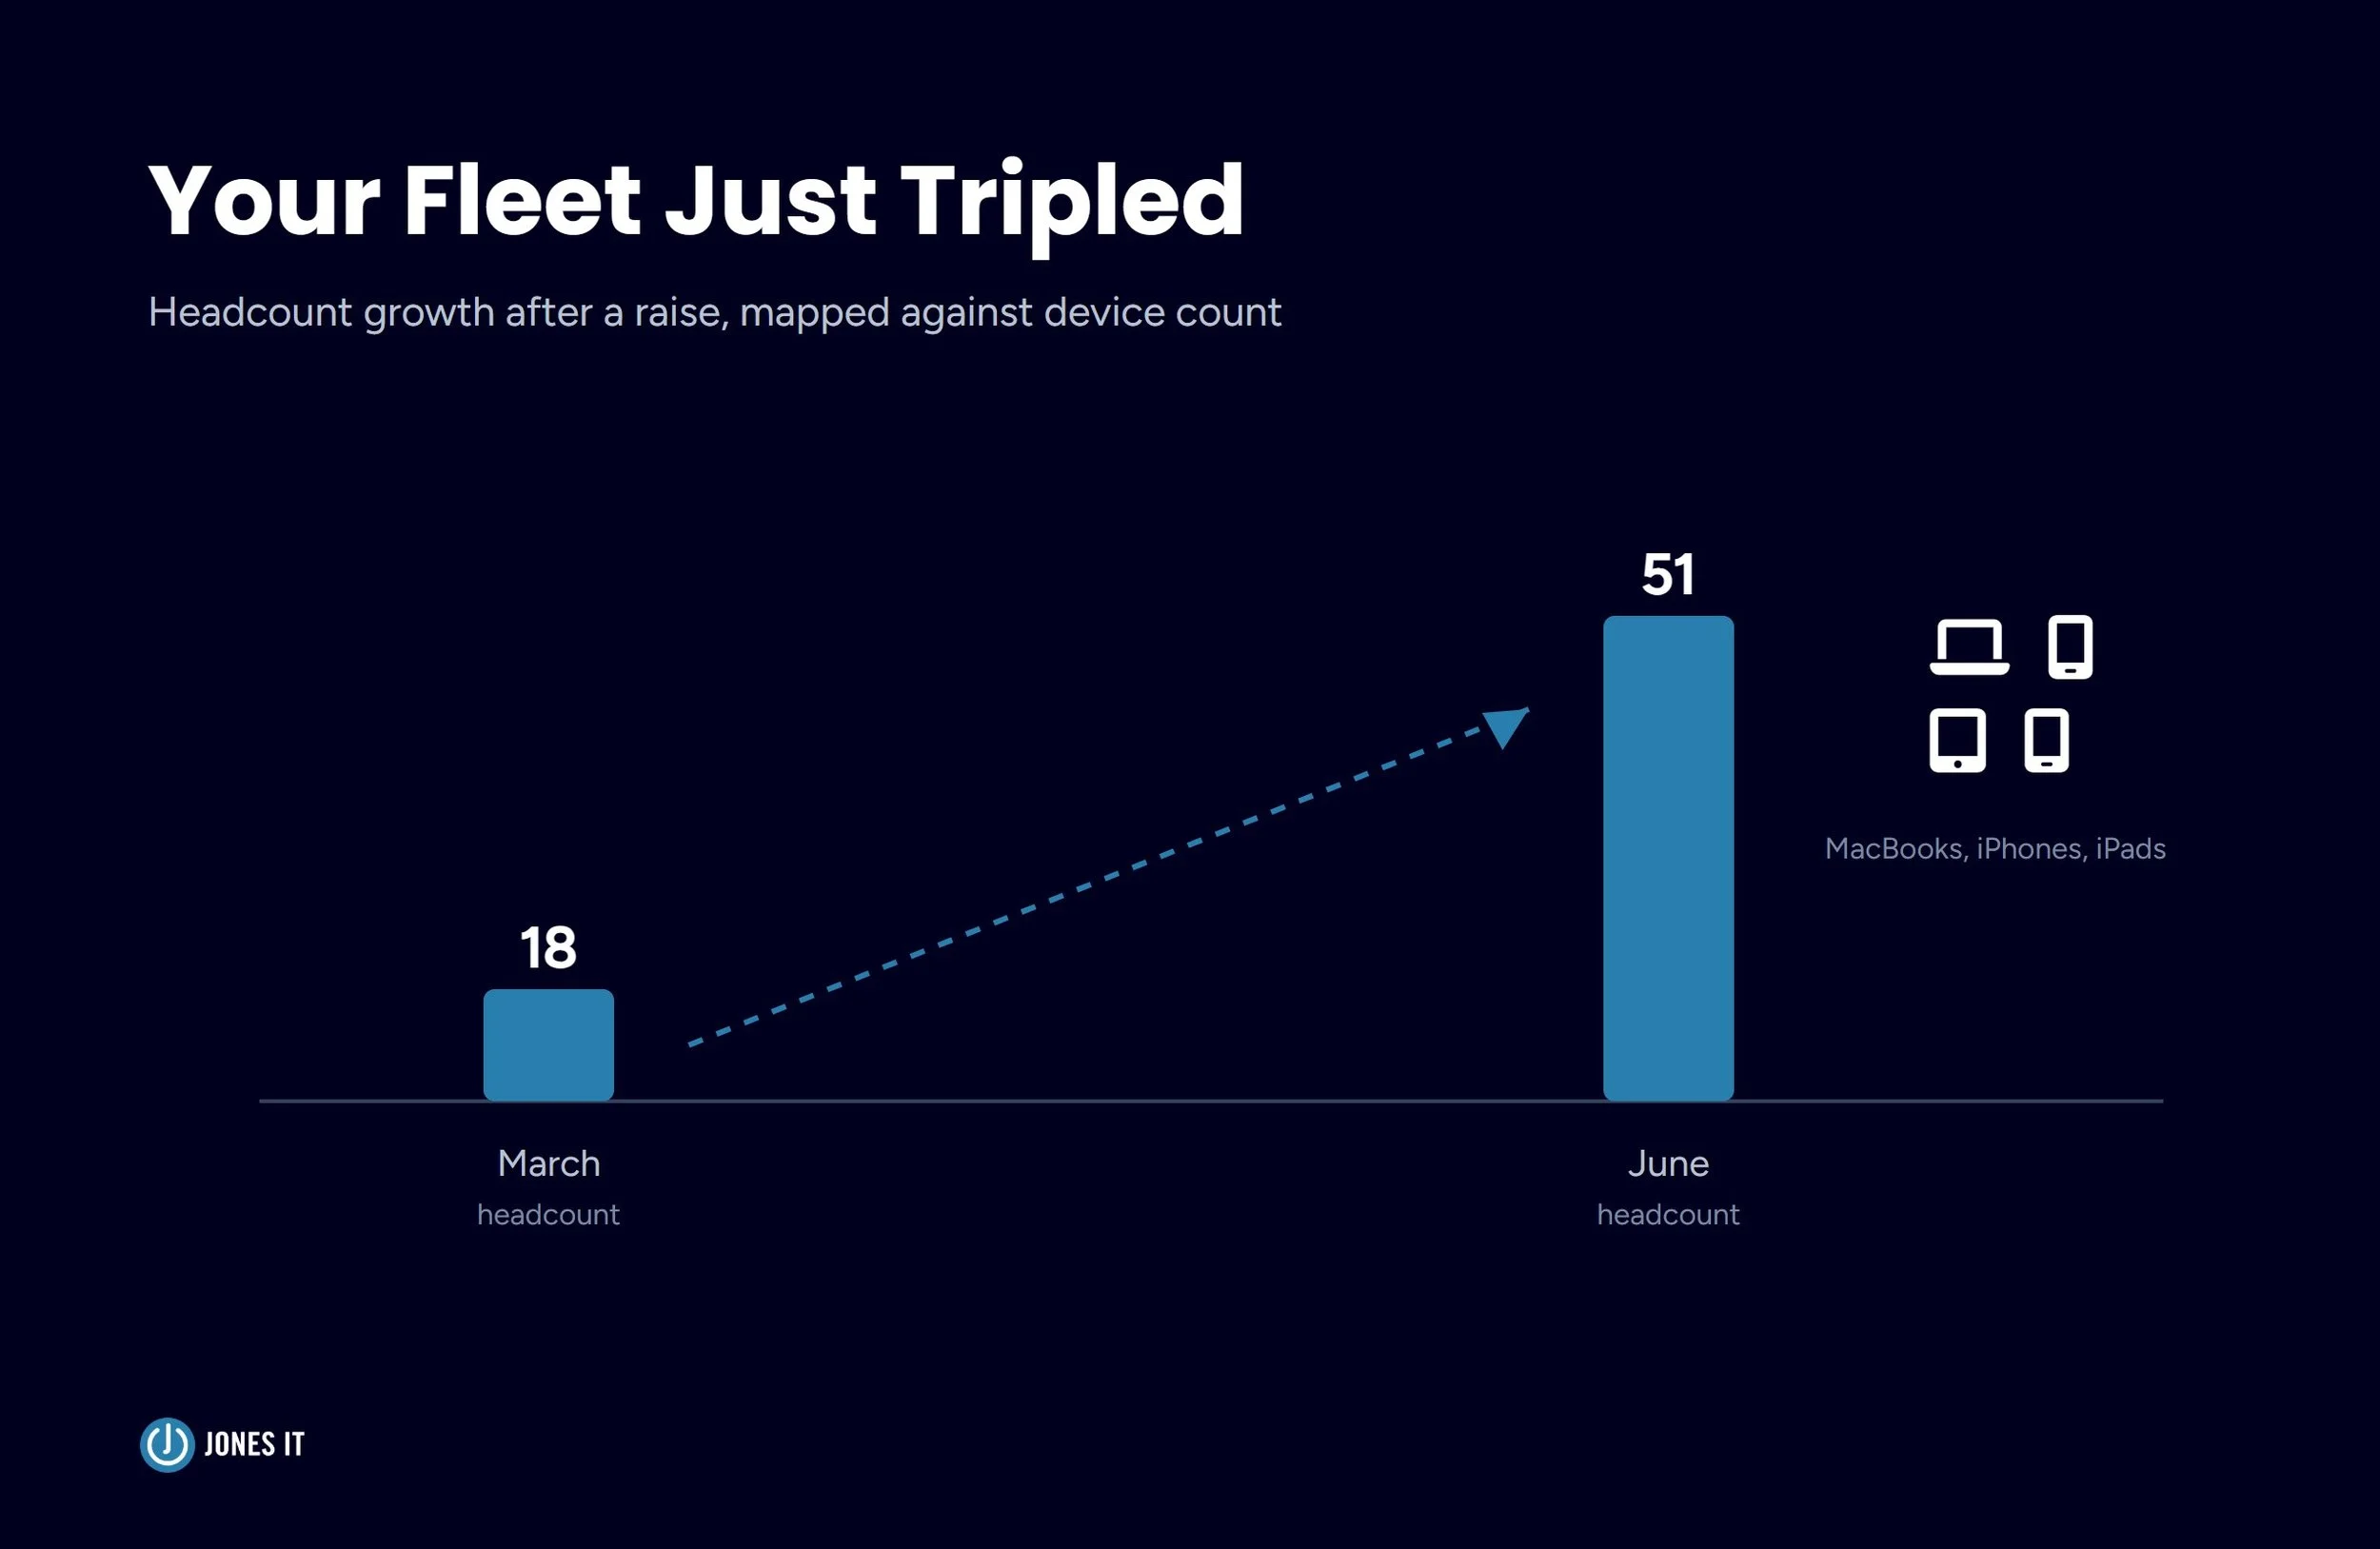
SOC 2 Device Access Controls for Your Apple Fleet
Secure your growing Apple fleet for SOC 2 compliance. Learn how to move beyond shared passwords to certificate-based auth and network segmentation.
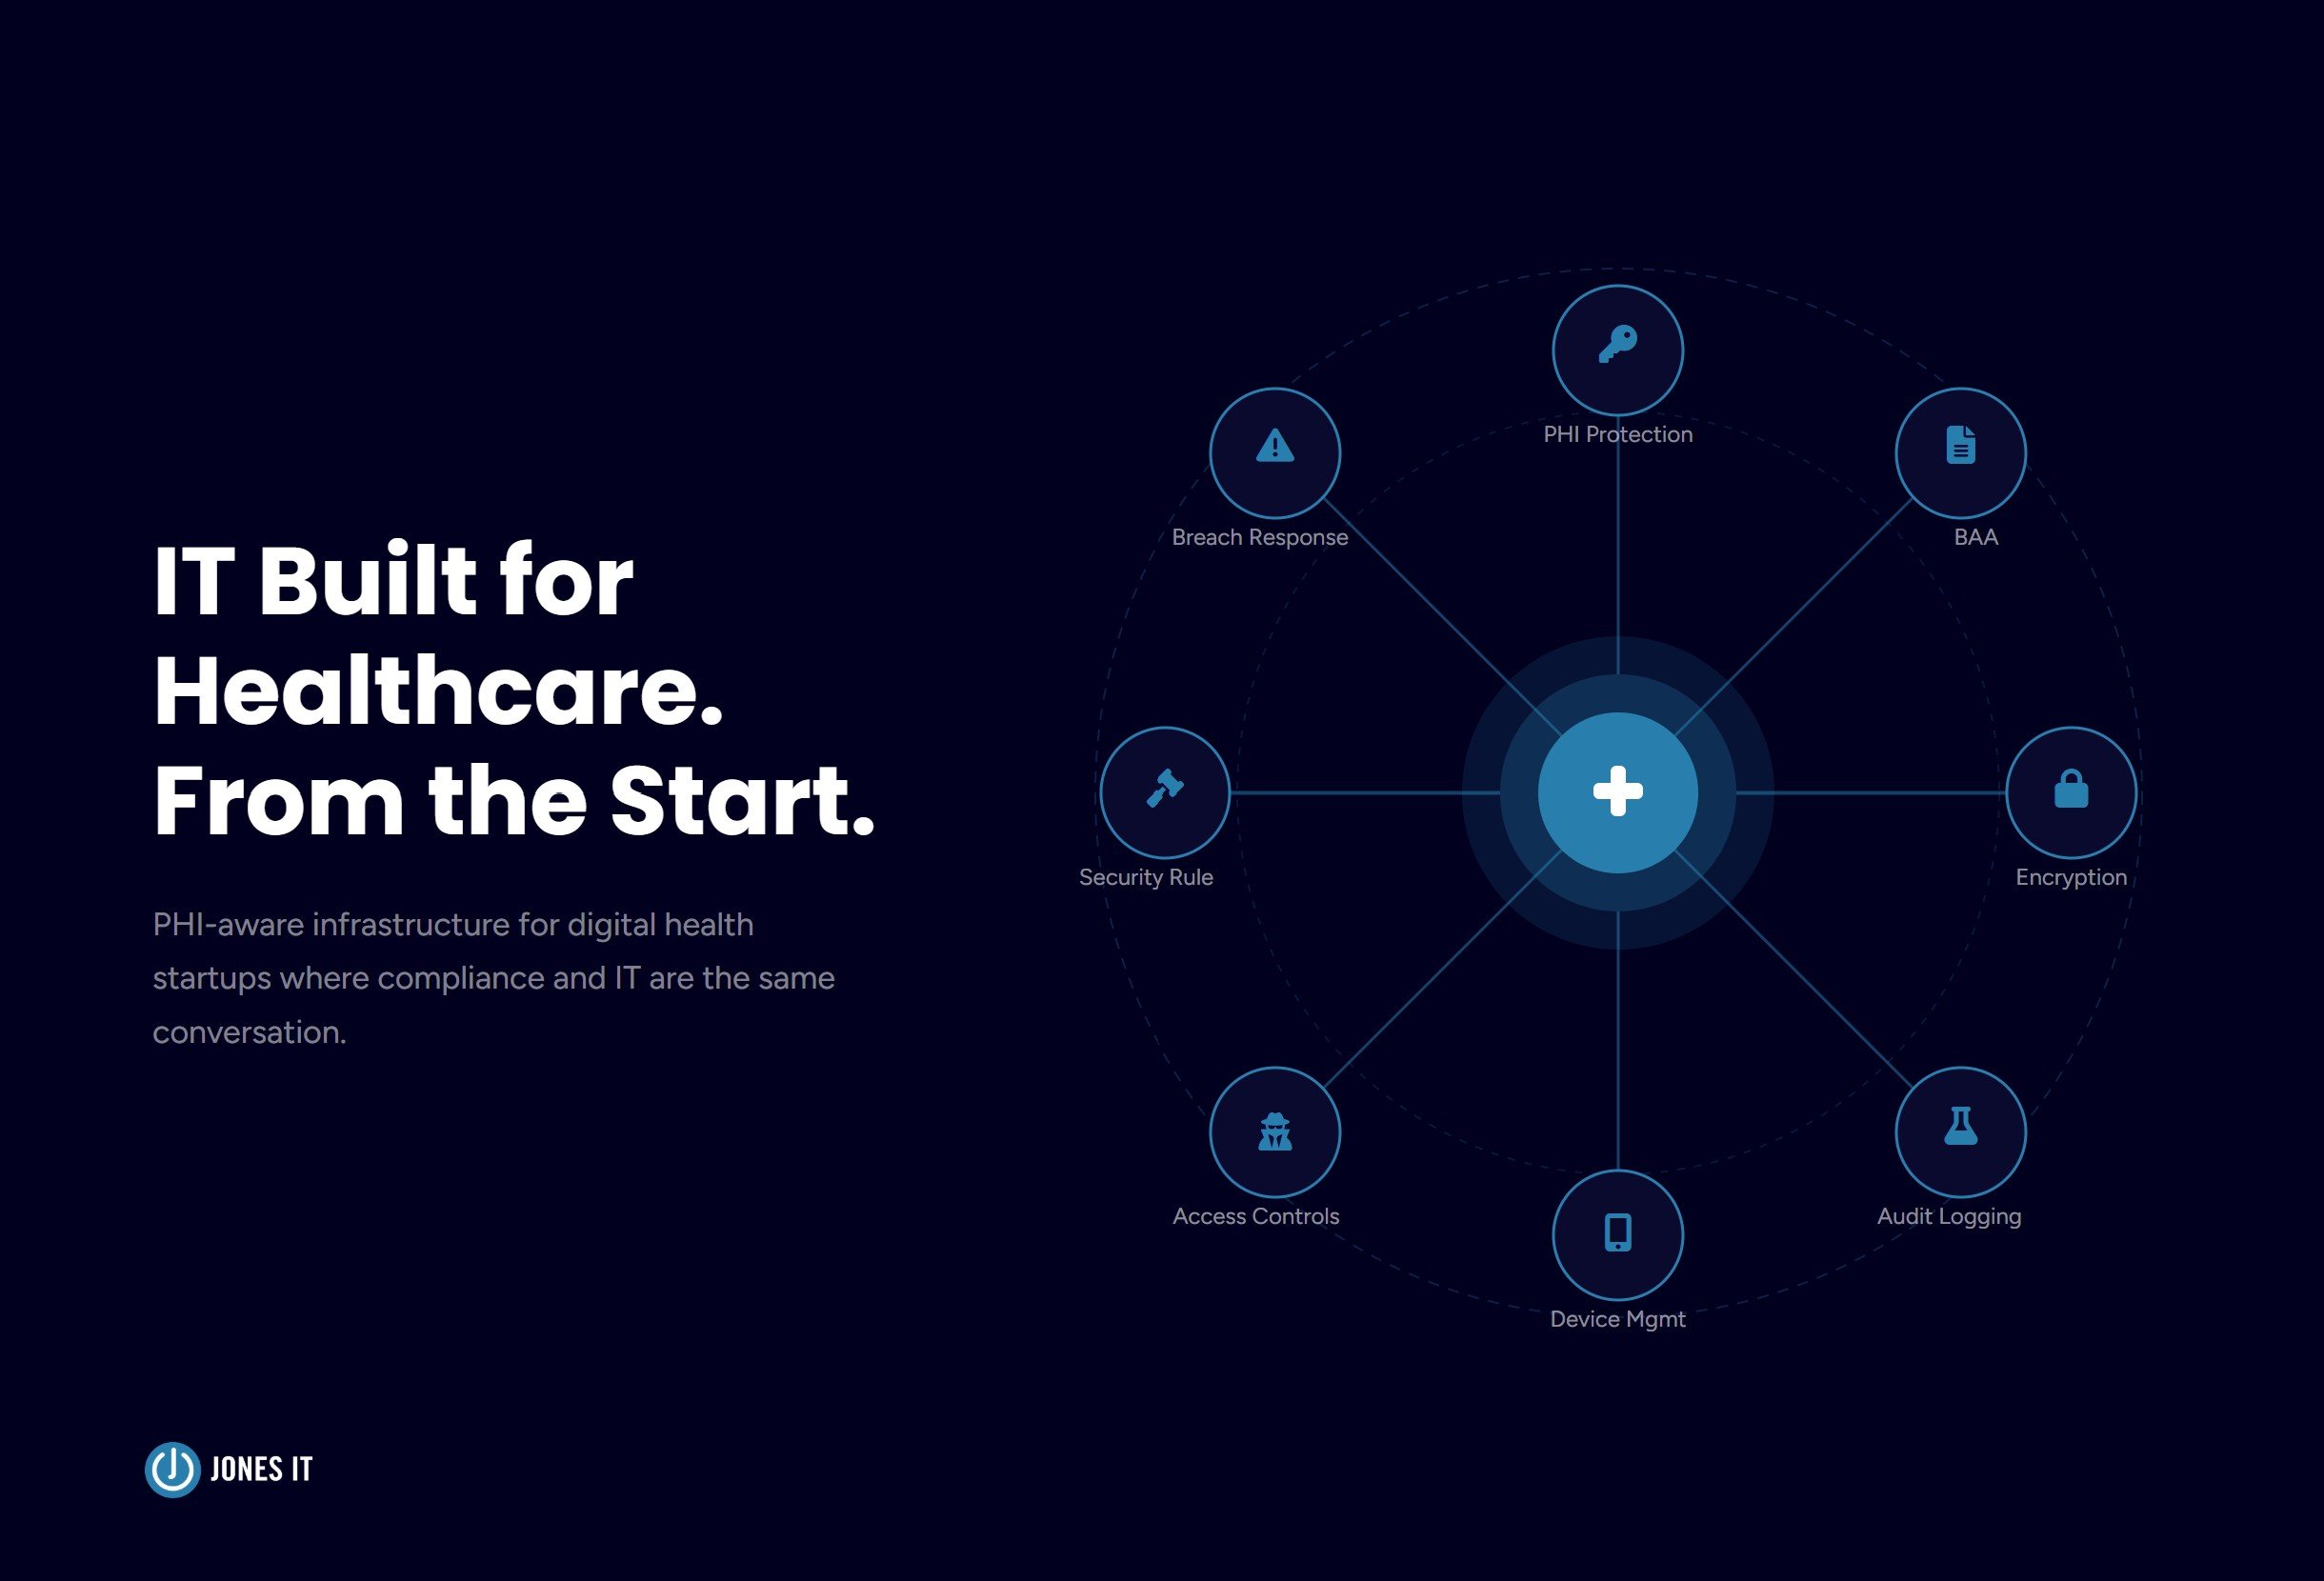
HIPAA-Compliant IT Support for Healthcare Startups: What to Require From Your MSP
Handling PHI? Standard IT support isn't enough. Learn the essential HIPAA security controls your healthcare startup must require from its MSP to stay compliant.
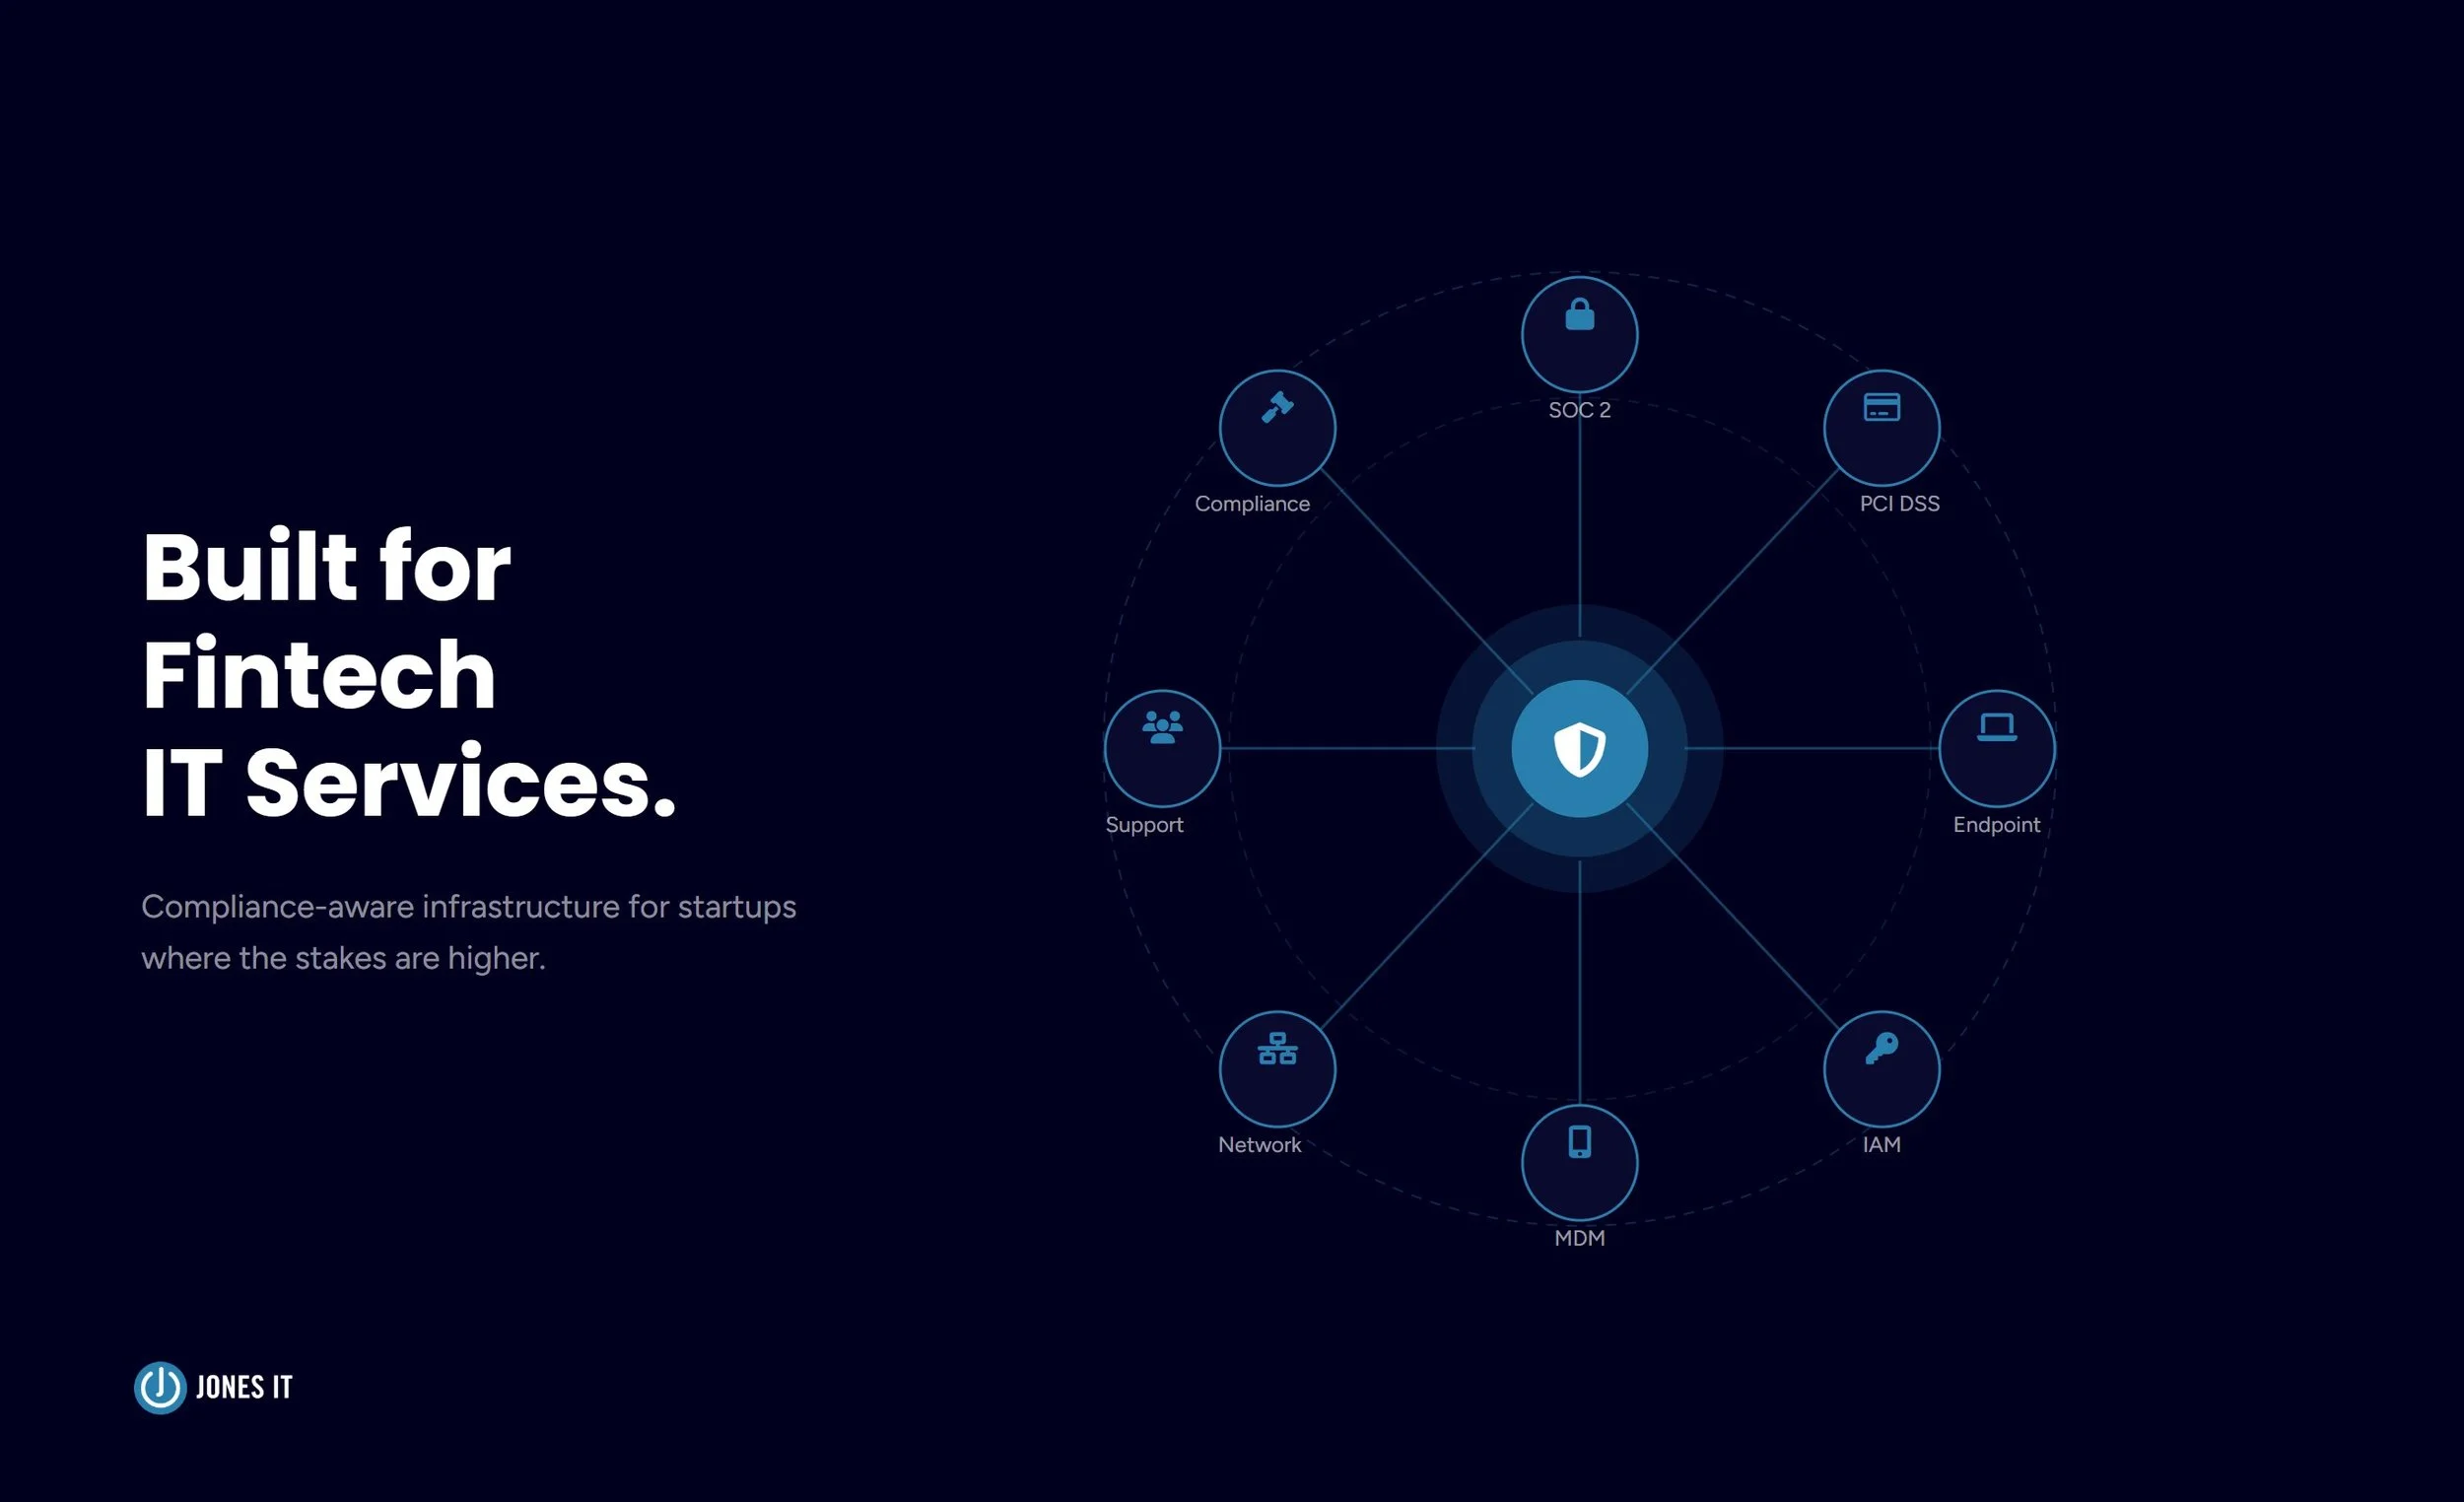
Managed IT Services for Fintech Startups: What You Need Before You Scale
Fintech startups face tighter compliance and scaling pressure. Here is what managed IT for fintech looks like, & what to require from your MSP before you scale.
IT Due Diligence Checklist: What Investors Audit Before Funding
Don't let technical audits kill your funding round. Learn the exact IT due diligence checklist investors use to audit startups: from IP assignment to SOC 2 compliance.
CCPA Compliance in 2026: What Your Startup Must Know
CCPA compliance changed in 2026 with new rules on opt-outs, risk assessments, and ADMT. Learn whether the California privacy law applies to your startup.
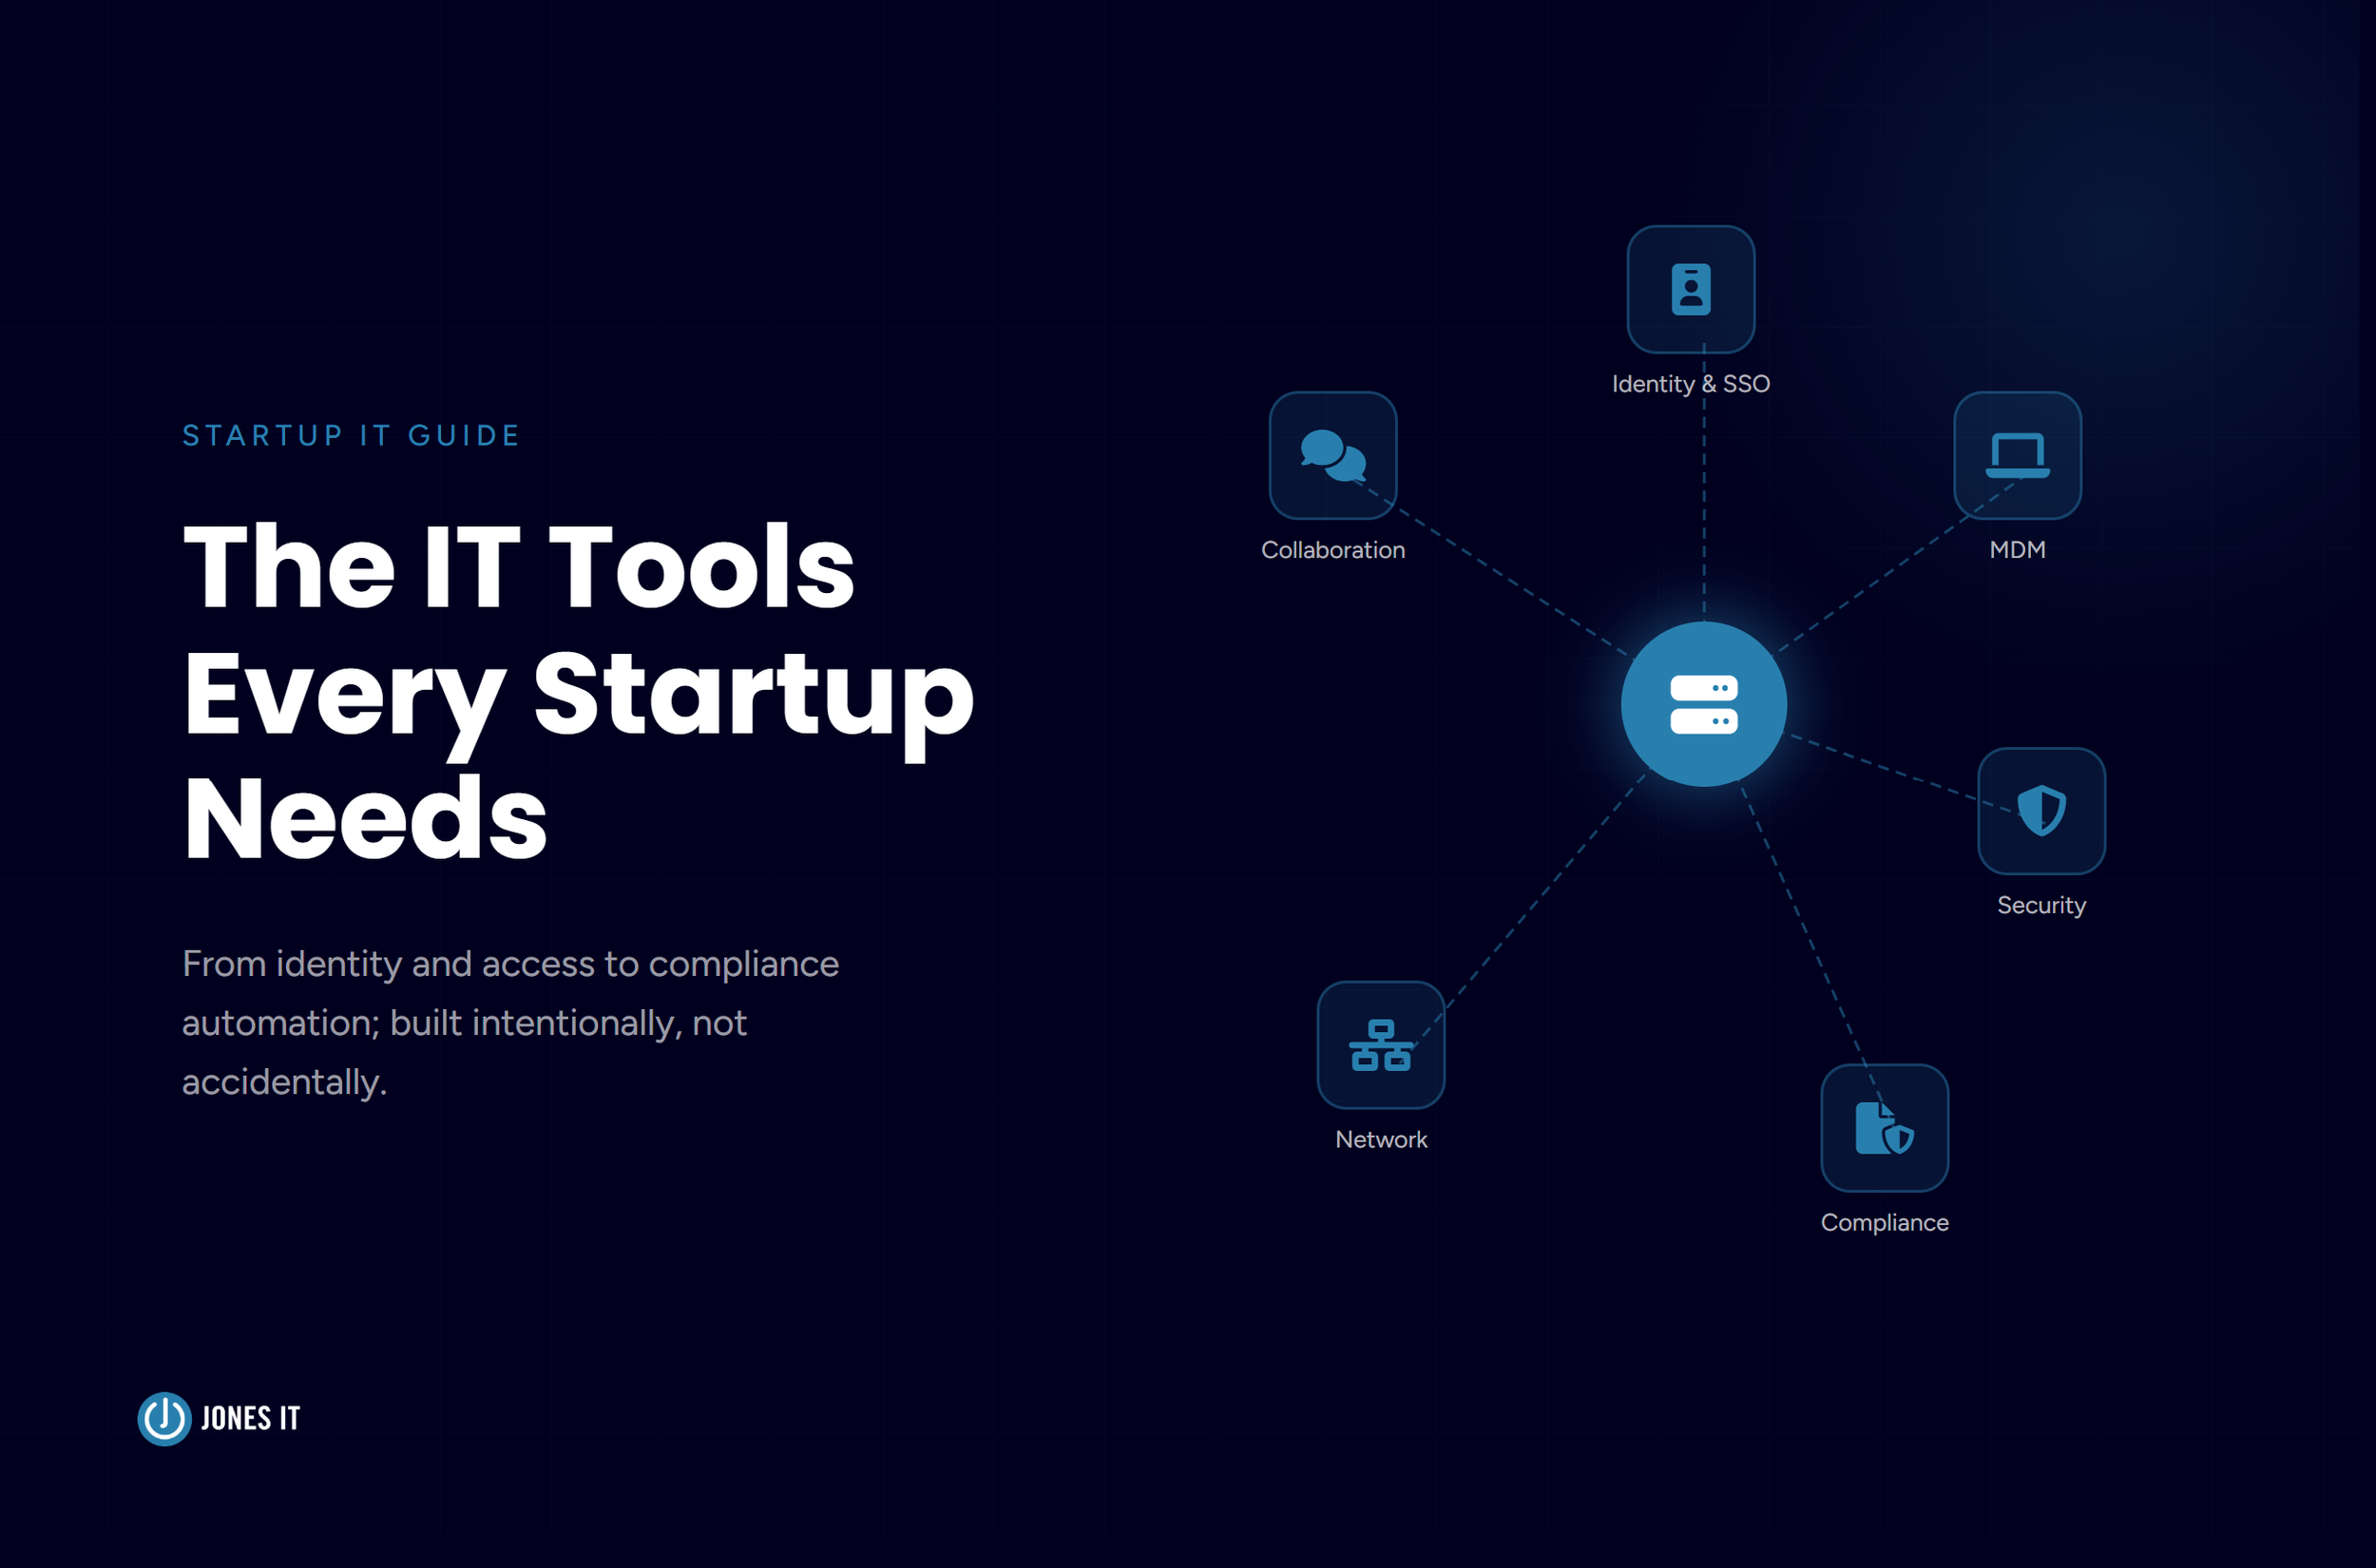
The IT Tools Every Startup Needs (And When to Add Them)
Build your startup's IT stack intentionally. Jones IT shares the essential tools every startup needs and the right time to implement them for long-term growth.
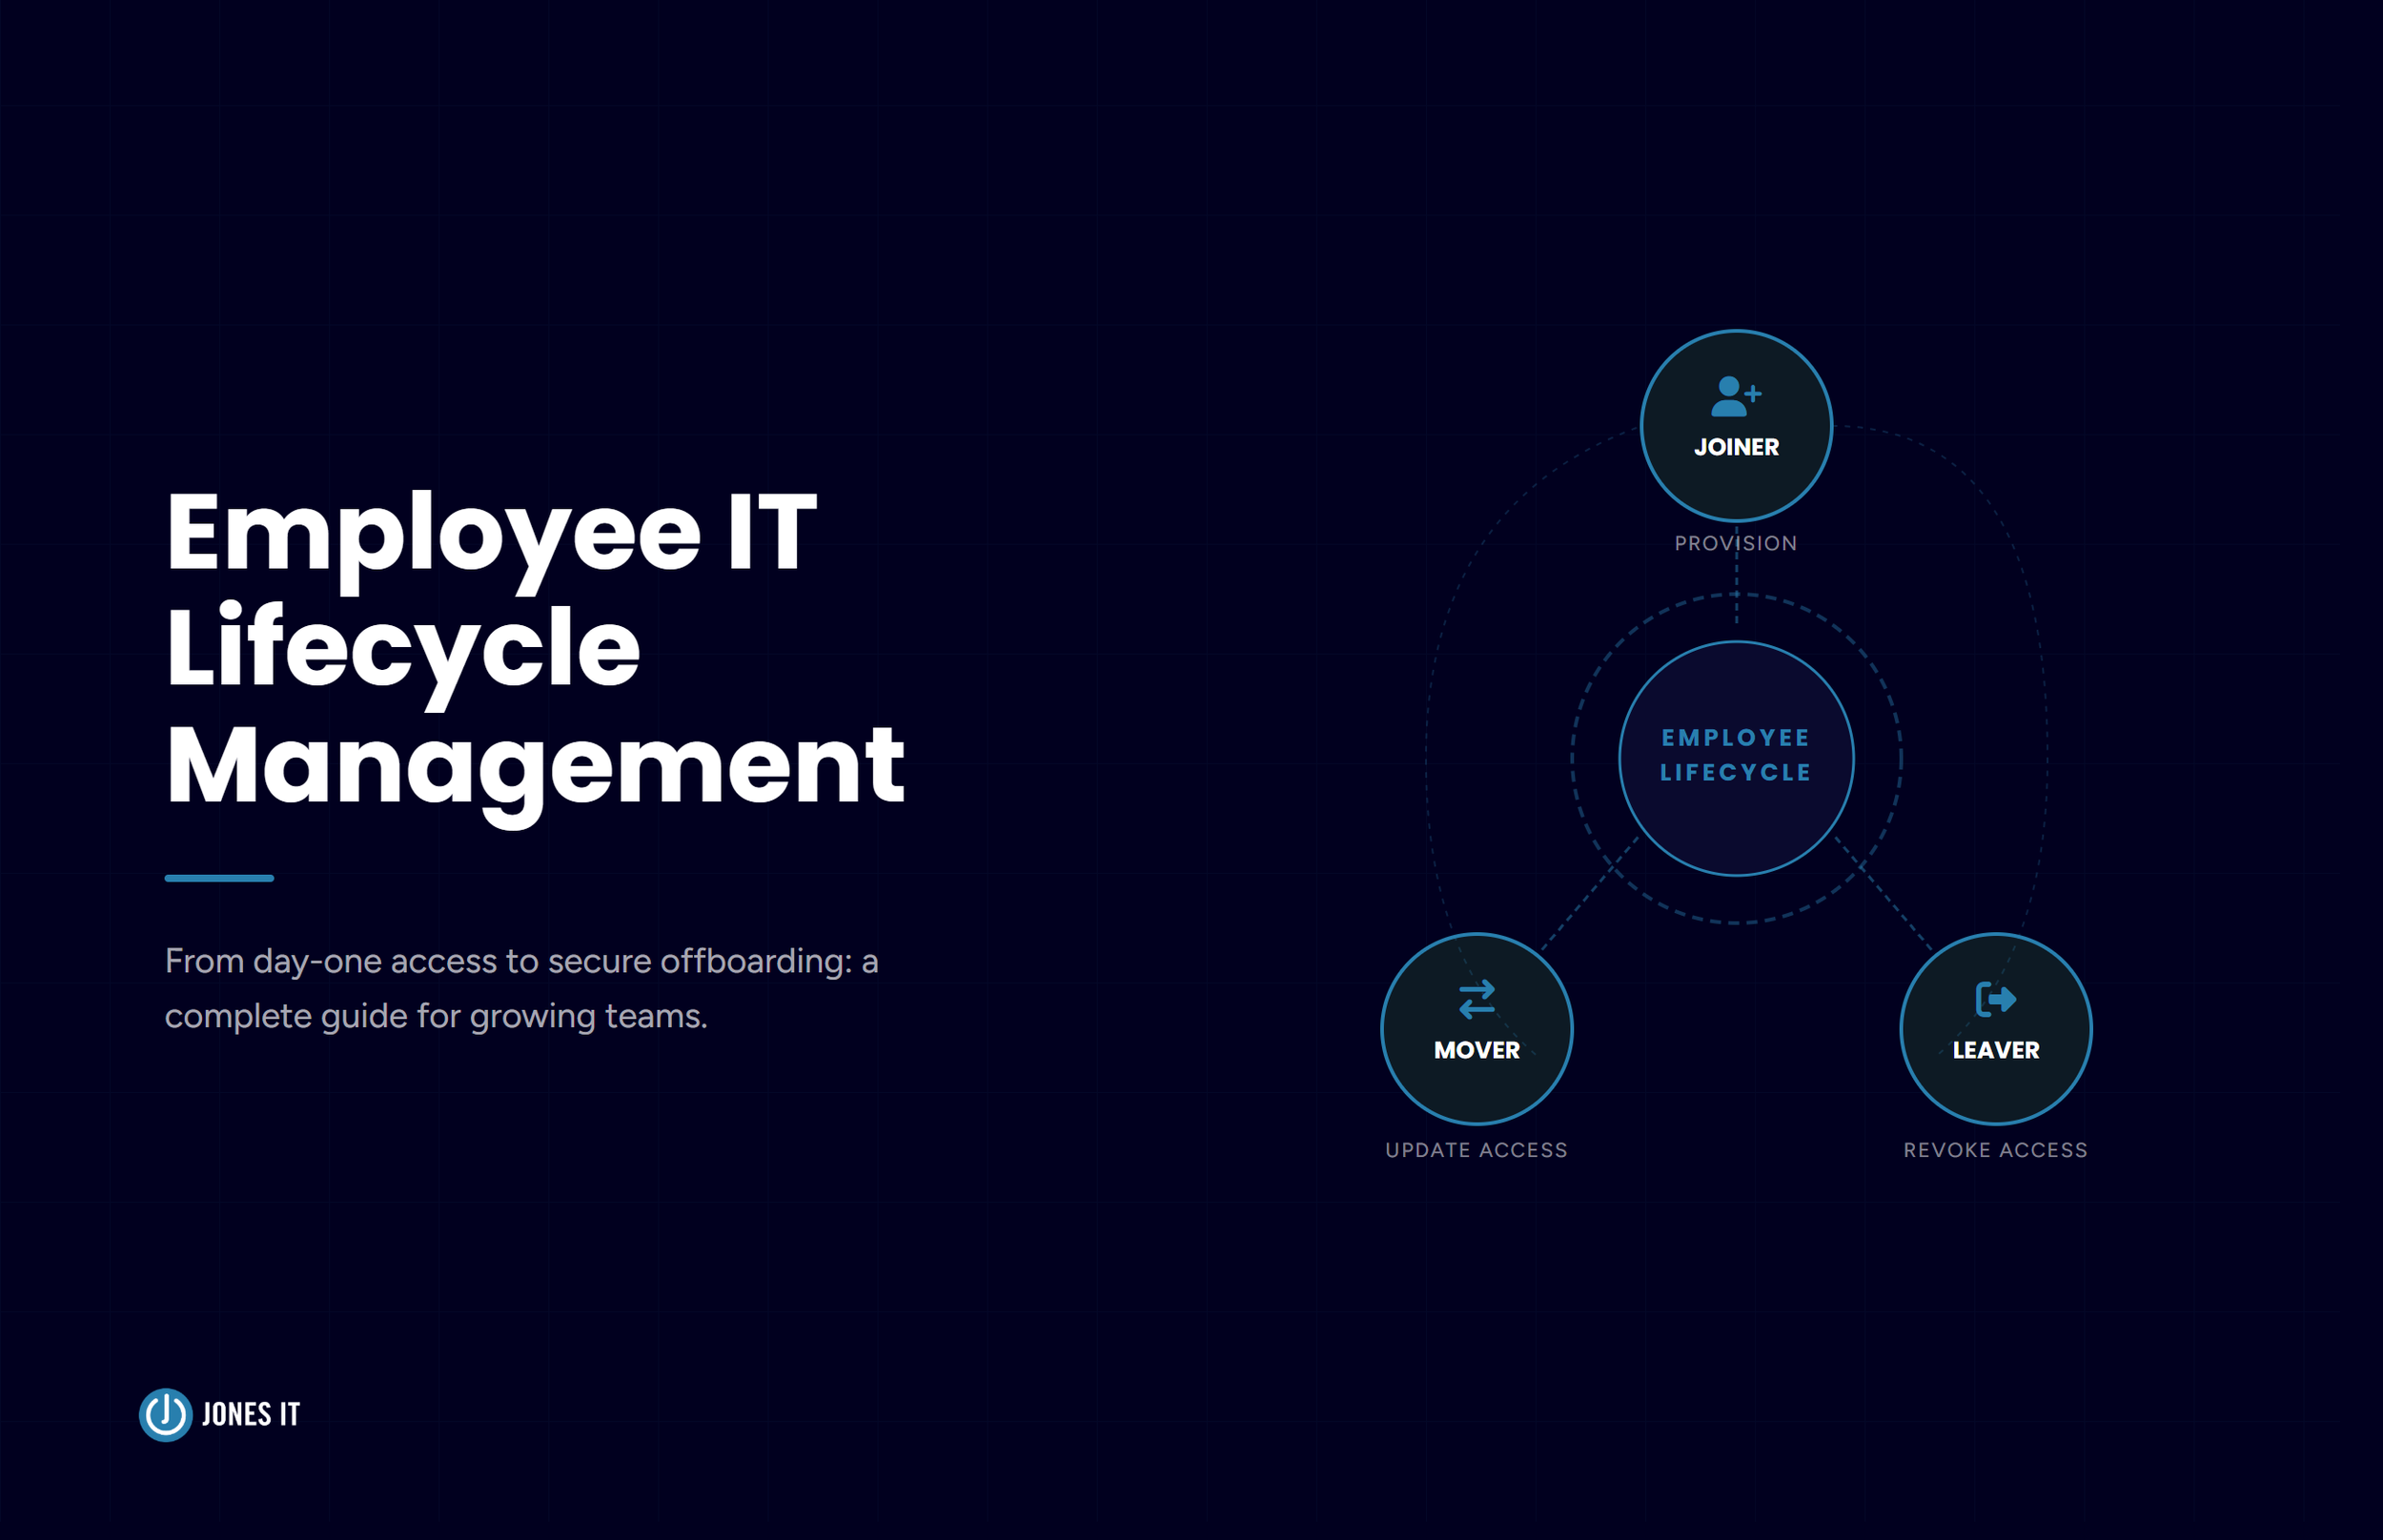
Employee IT Lifecycle Management: Onboarding, Roles, Offboarding
Employee IT lifecycle management: Provisioning, access updates, and offboarding. Build a process to keep new hires productive, prevent privilege creep, and close security gaps.
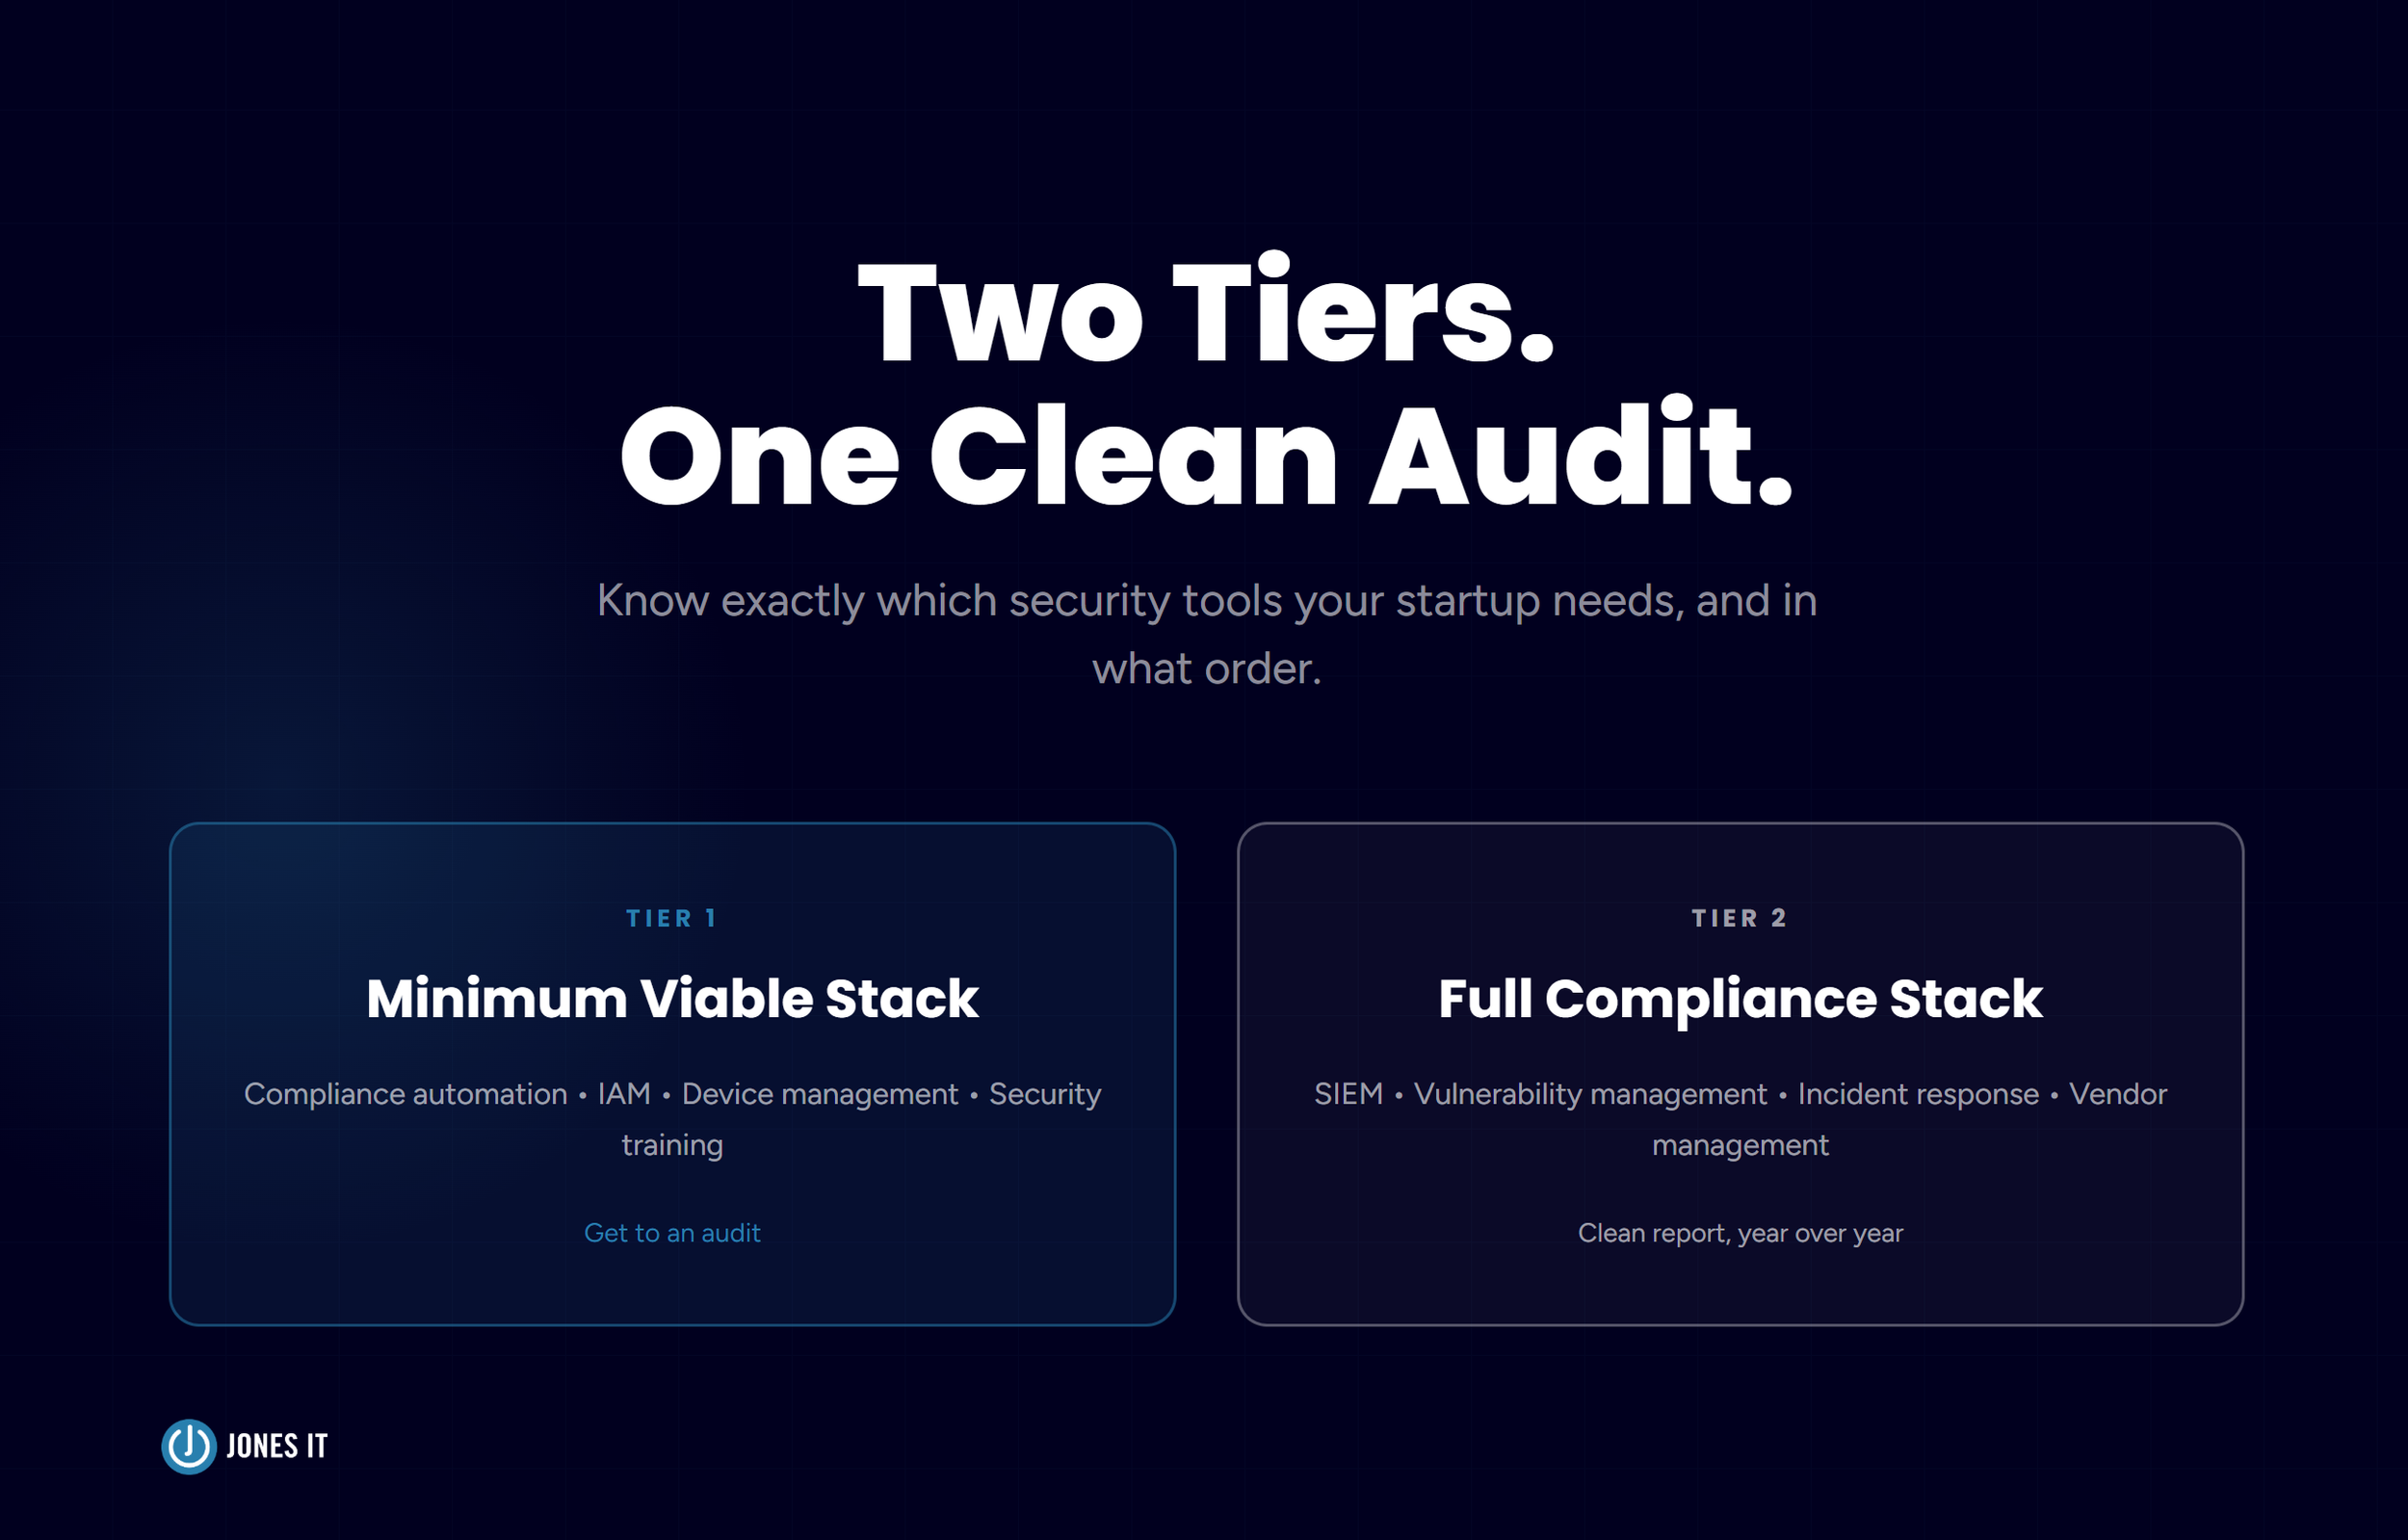
SOC 2 Compliance Tools: What Security Stack Does Your Startup Actually Need?
SOC 2 compliance tools don't have to be overwhelming. Learn exactly which security tools a Series A startup needs, from compliance automation to IAM and SIEM, and how to sequence your purchases before your observation period begins.
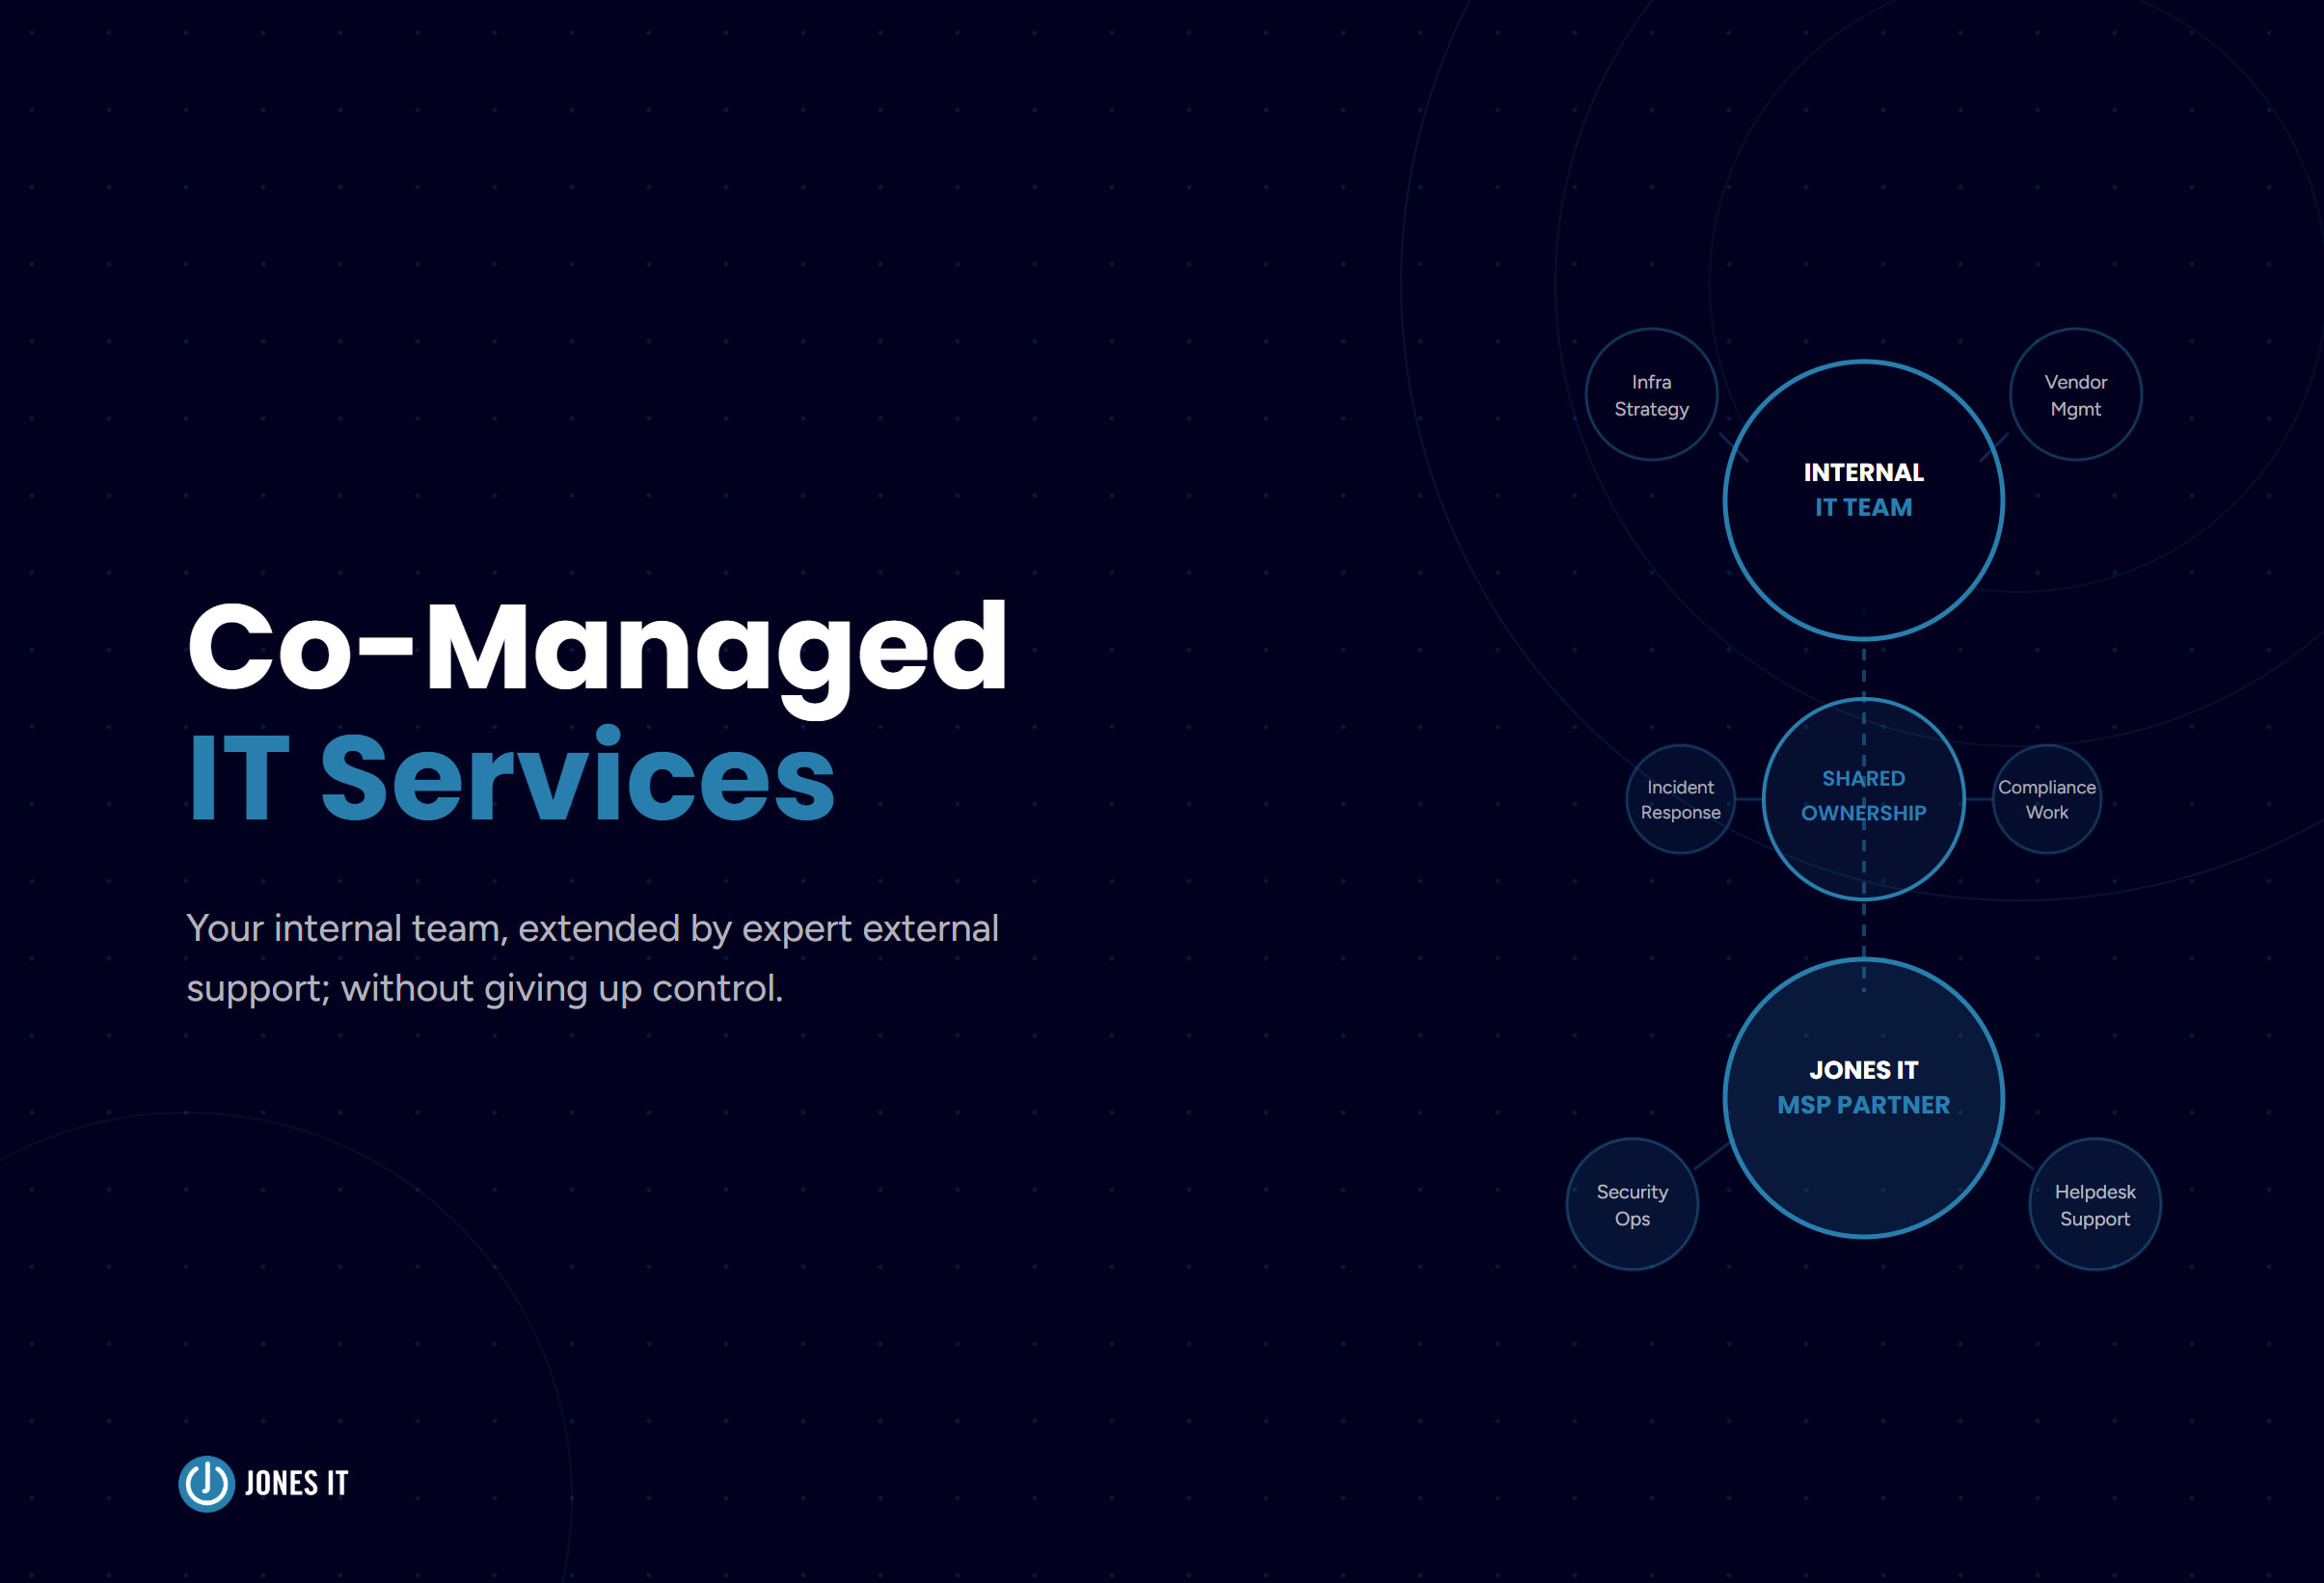
Co-Managed IT Services: 5 Signs Your IT Team Is Ready for One
Co-managed IT services let your internal team keep control while an MSP fills gaps in capacity, expertise, and compliance. Here's what the model looks like and when it makes sense for growing Bay Area tech companies.
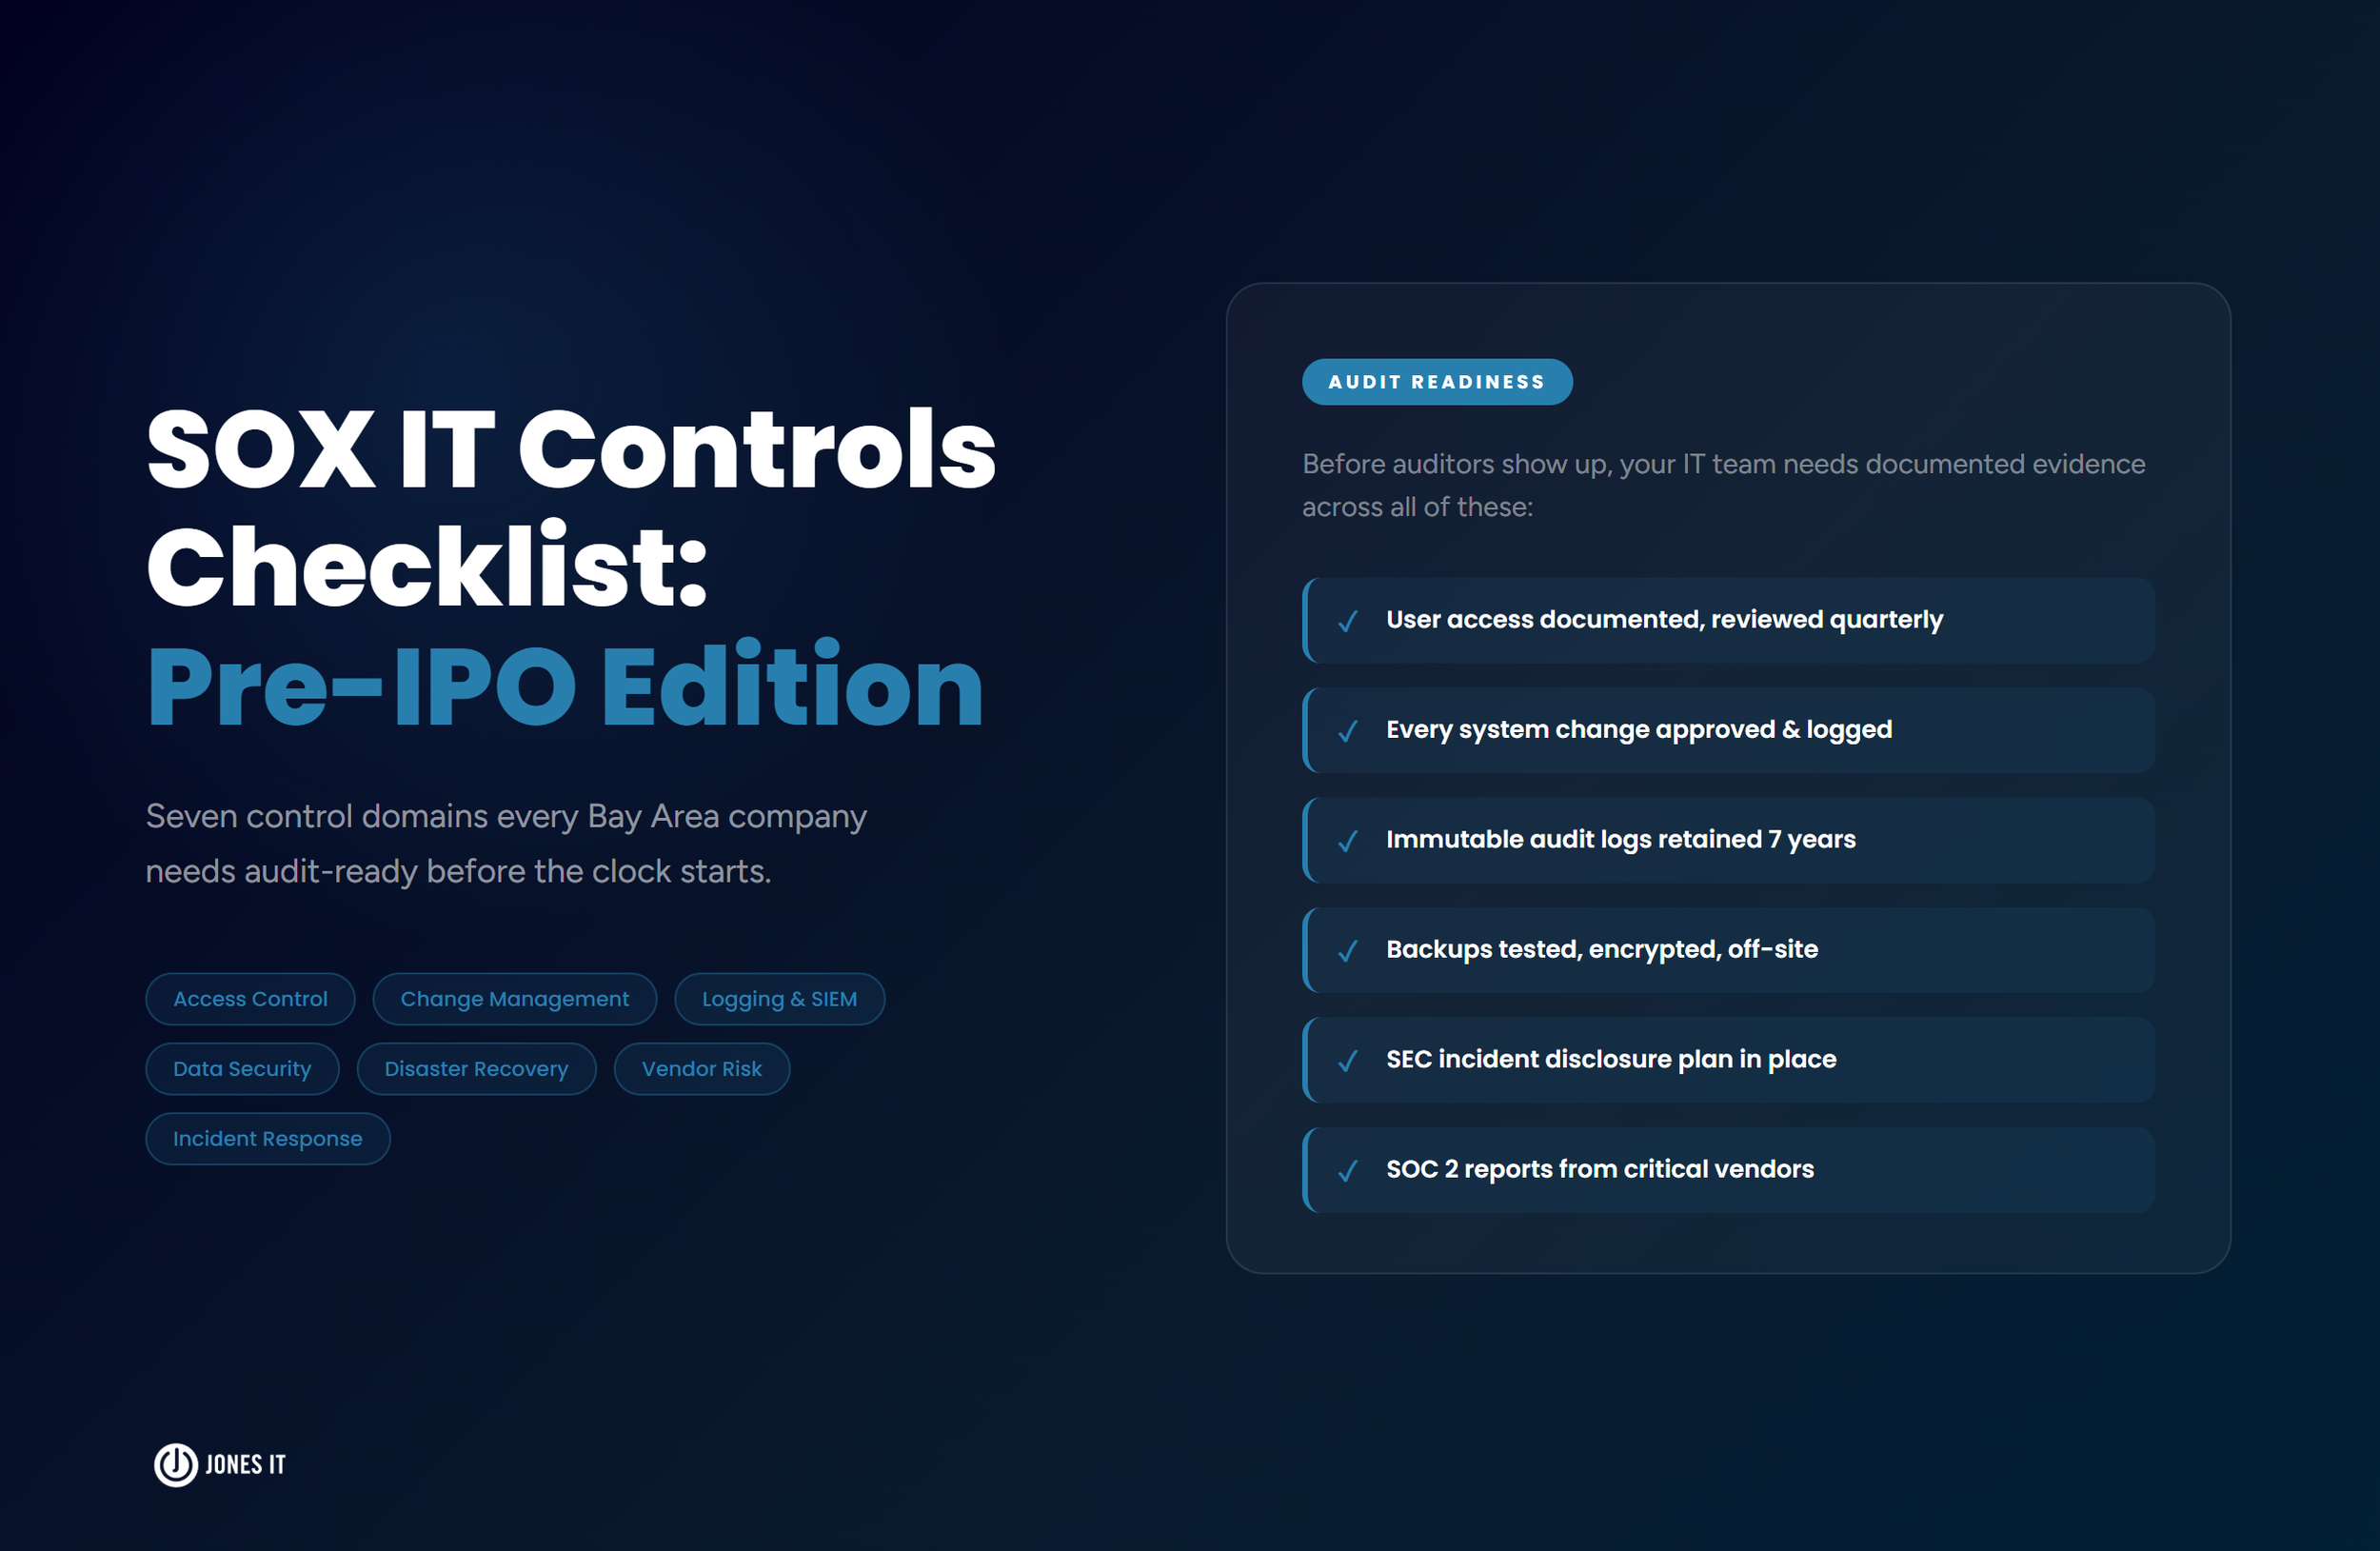
SOX IT Controls Checklist: What Every Pre-IPO Company Needs
The SOX IT controls checklist covers seven domains: access management, change management, logging, data security, disaster recovery, vendor risk, and incident response. Built for pre-IPO Bay Area companies getting audit-ready.
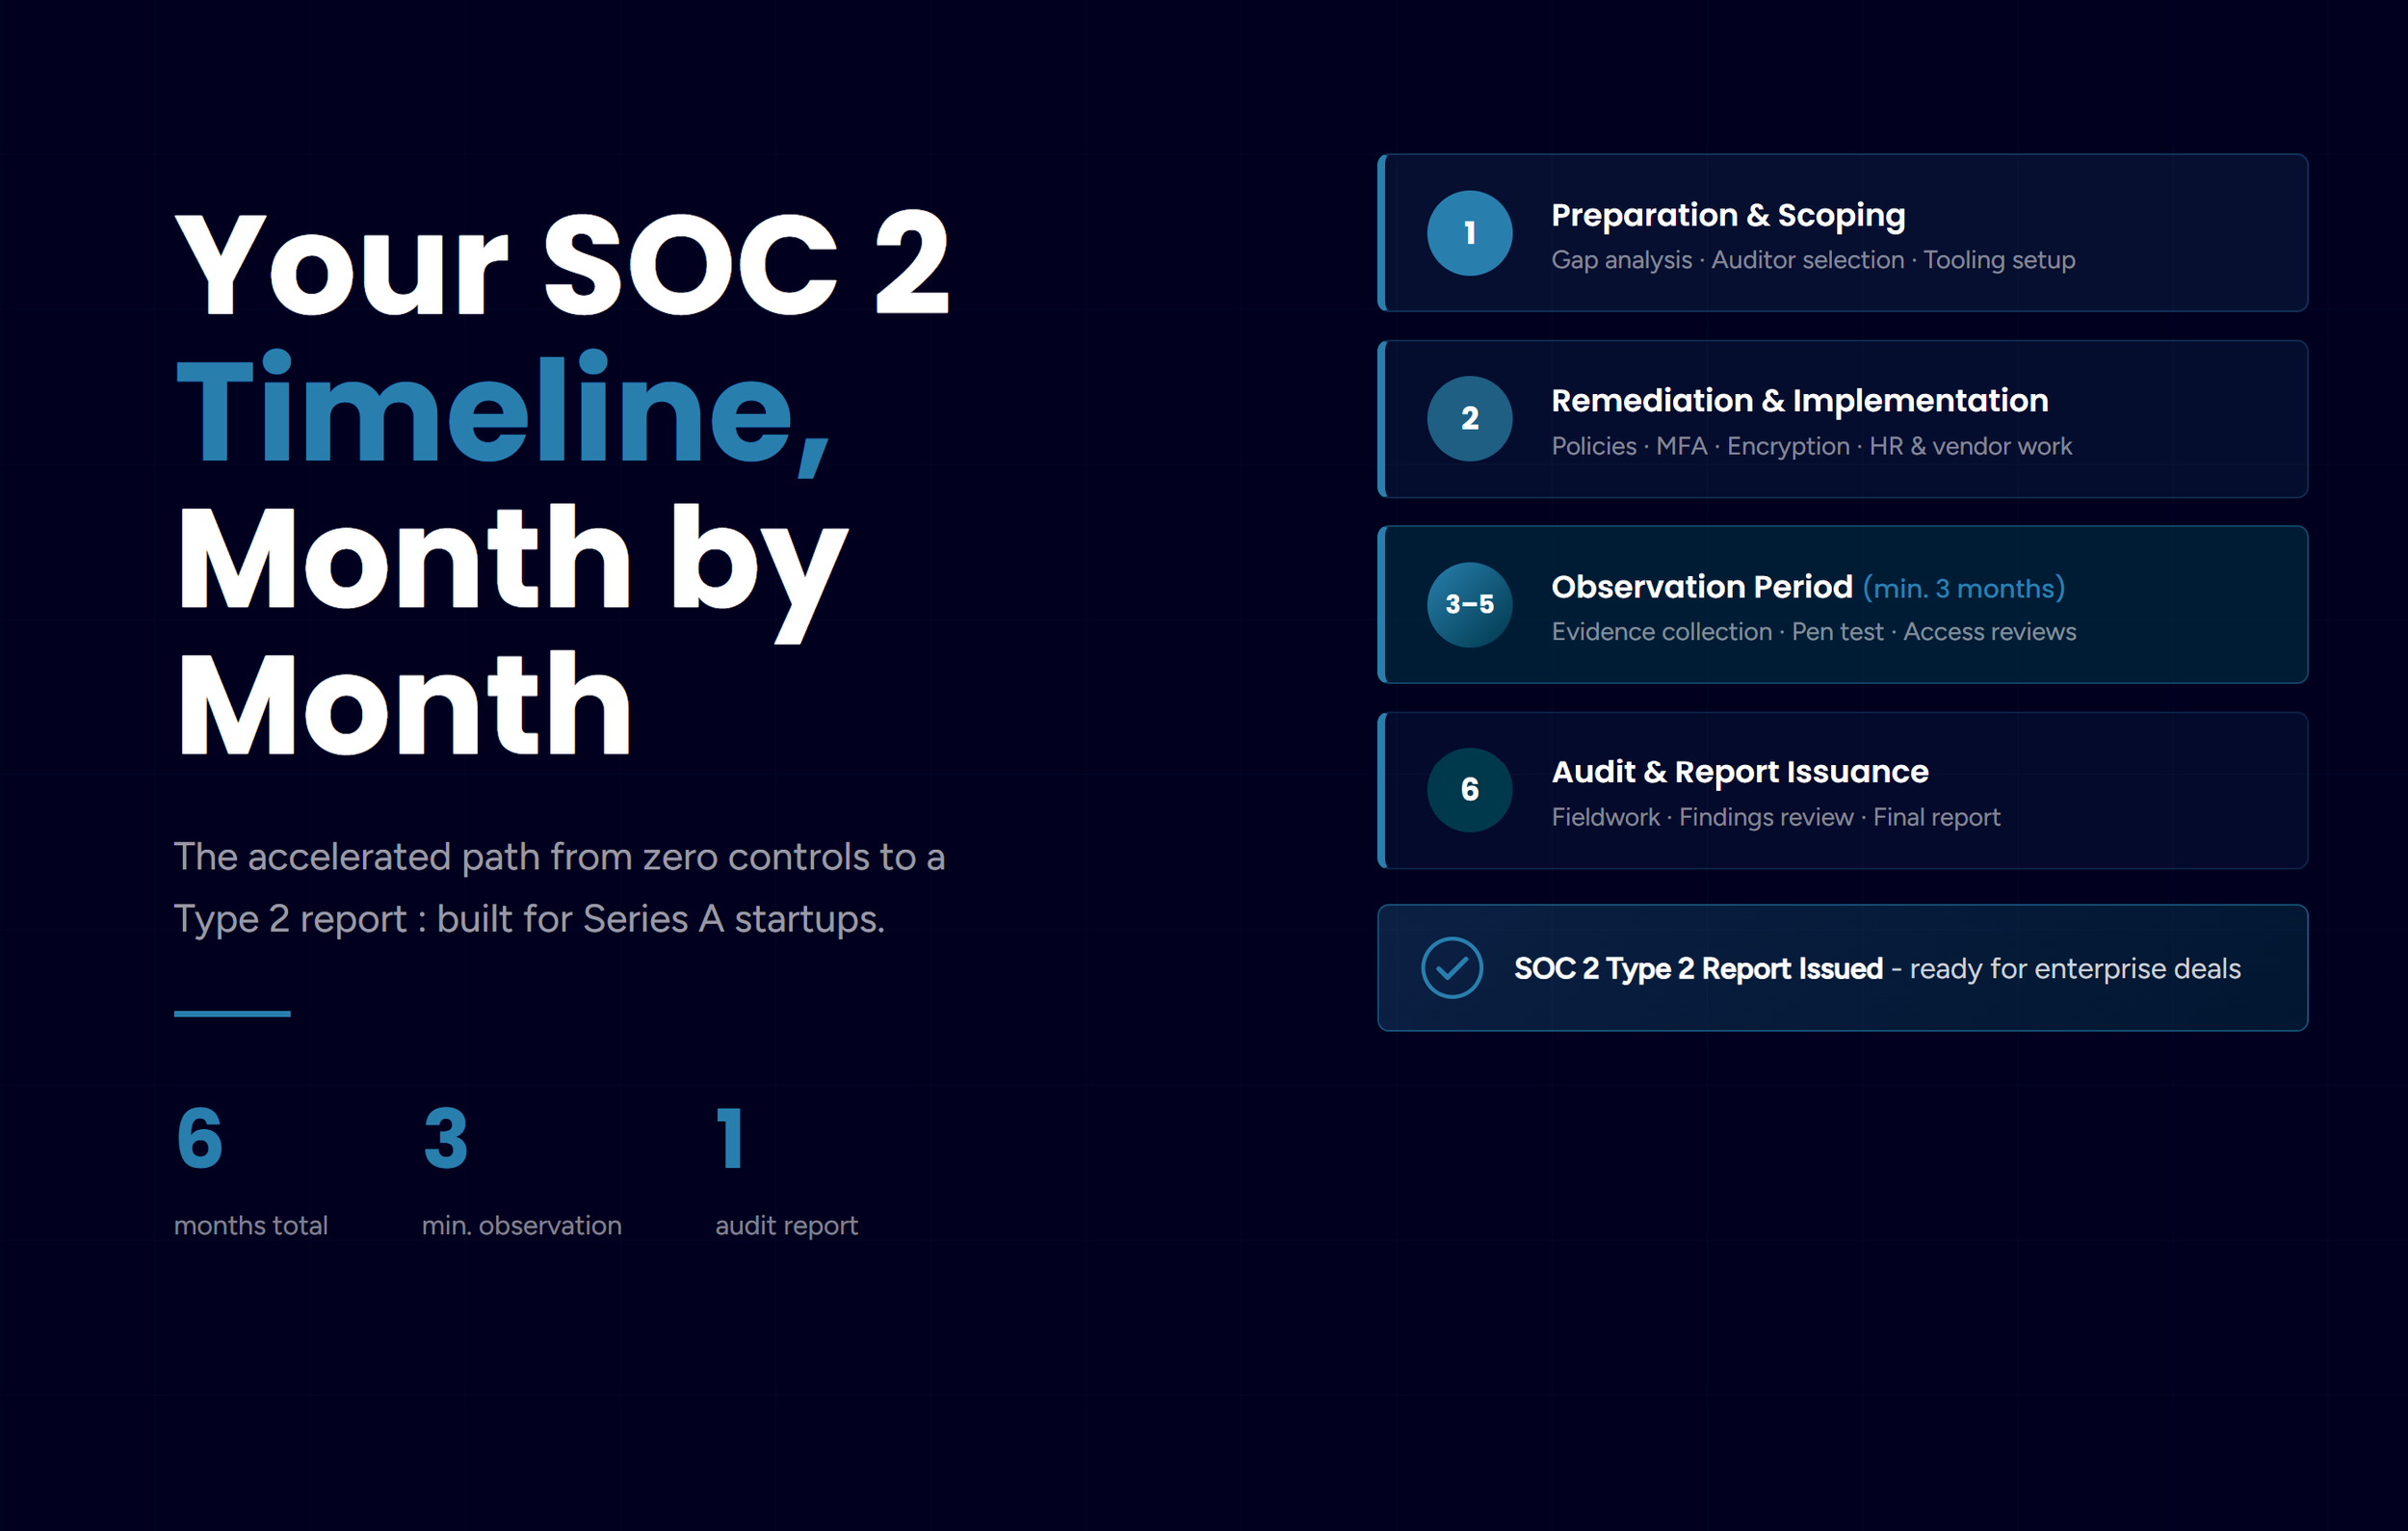
SOC 2 Compliance Timeline: Month-by-Month Roadmap for Series A Startups
A realistic month-by-month SOC 2 Type 2 roadmap for Series A startups, covering scoping, remediation, the observation period, and audit. Includes budget estimates and the pitfalls to avoid.

SOC 2 Type 1 vs Type 2: Which Does Your Startup Actually Need?
SOC 2 Type 1 vs Type 2: Jones IT explains the key differences, when each type makes sense for startups, and how to choose the right path for enterprise sales.
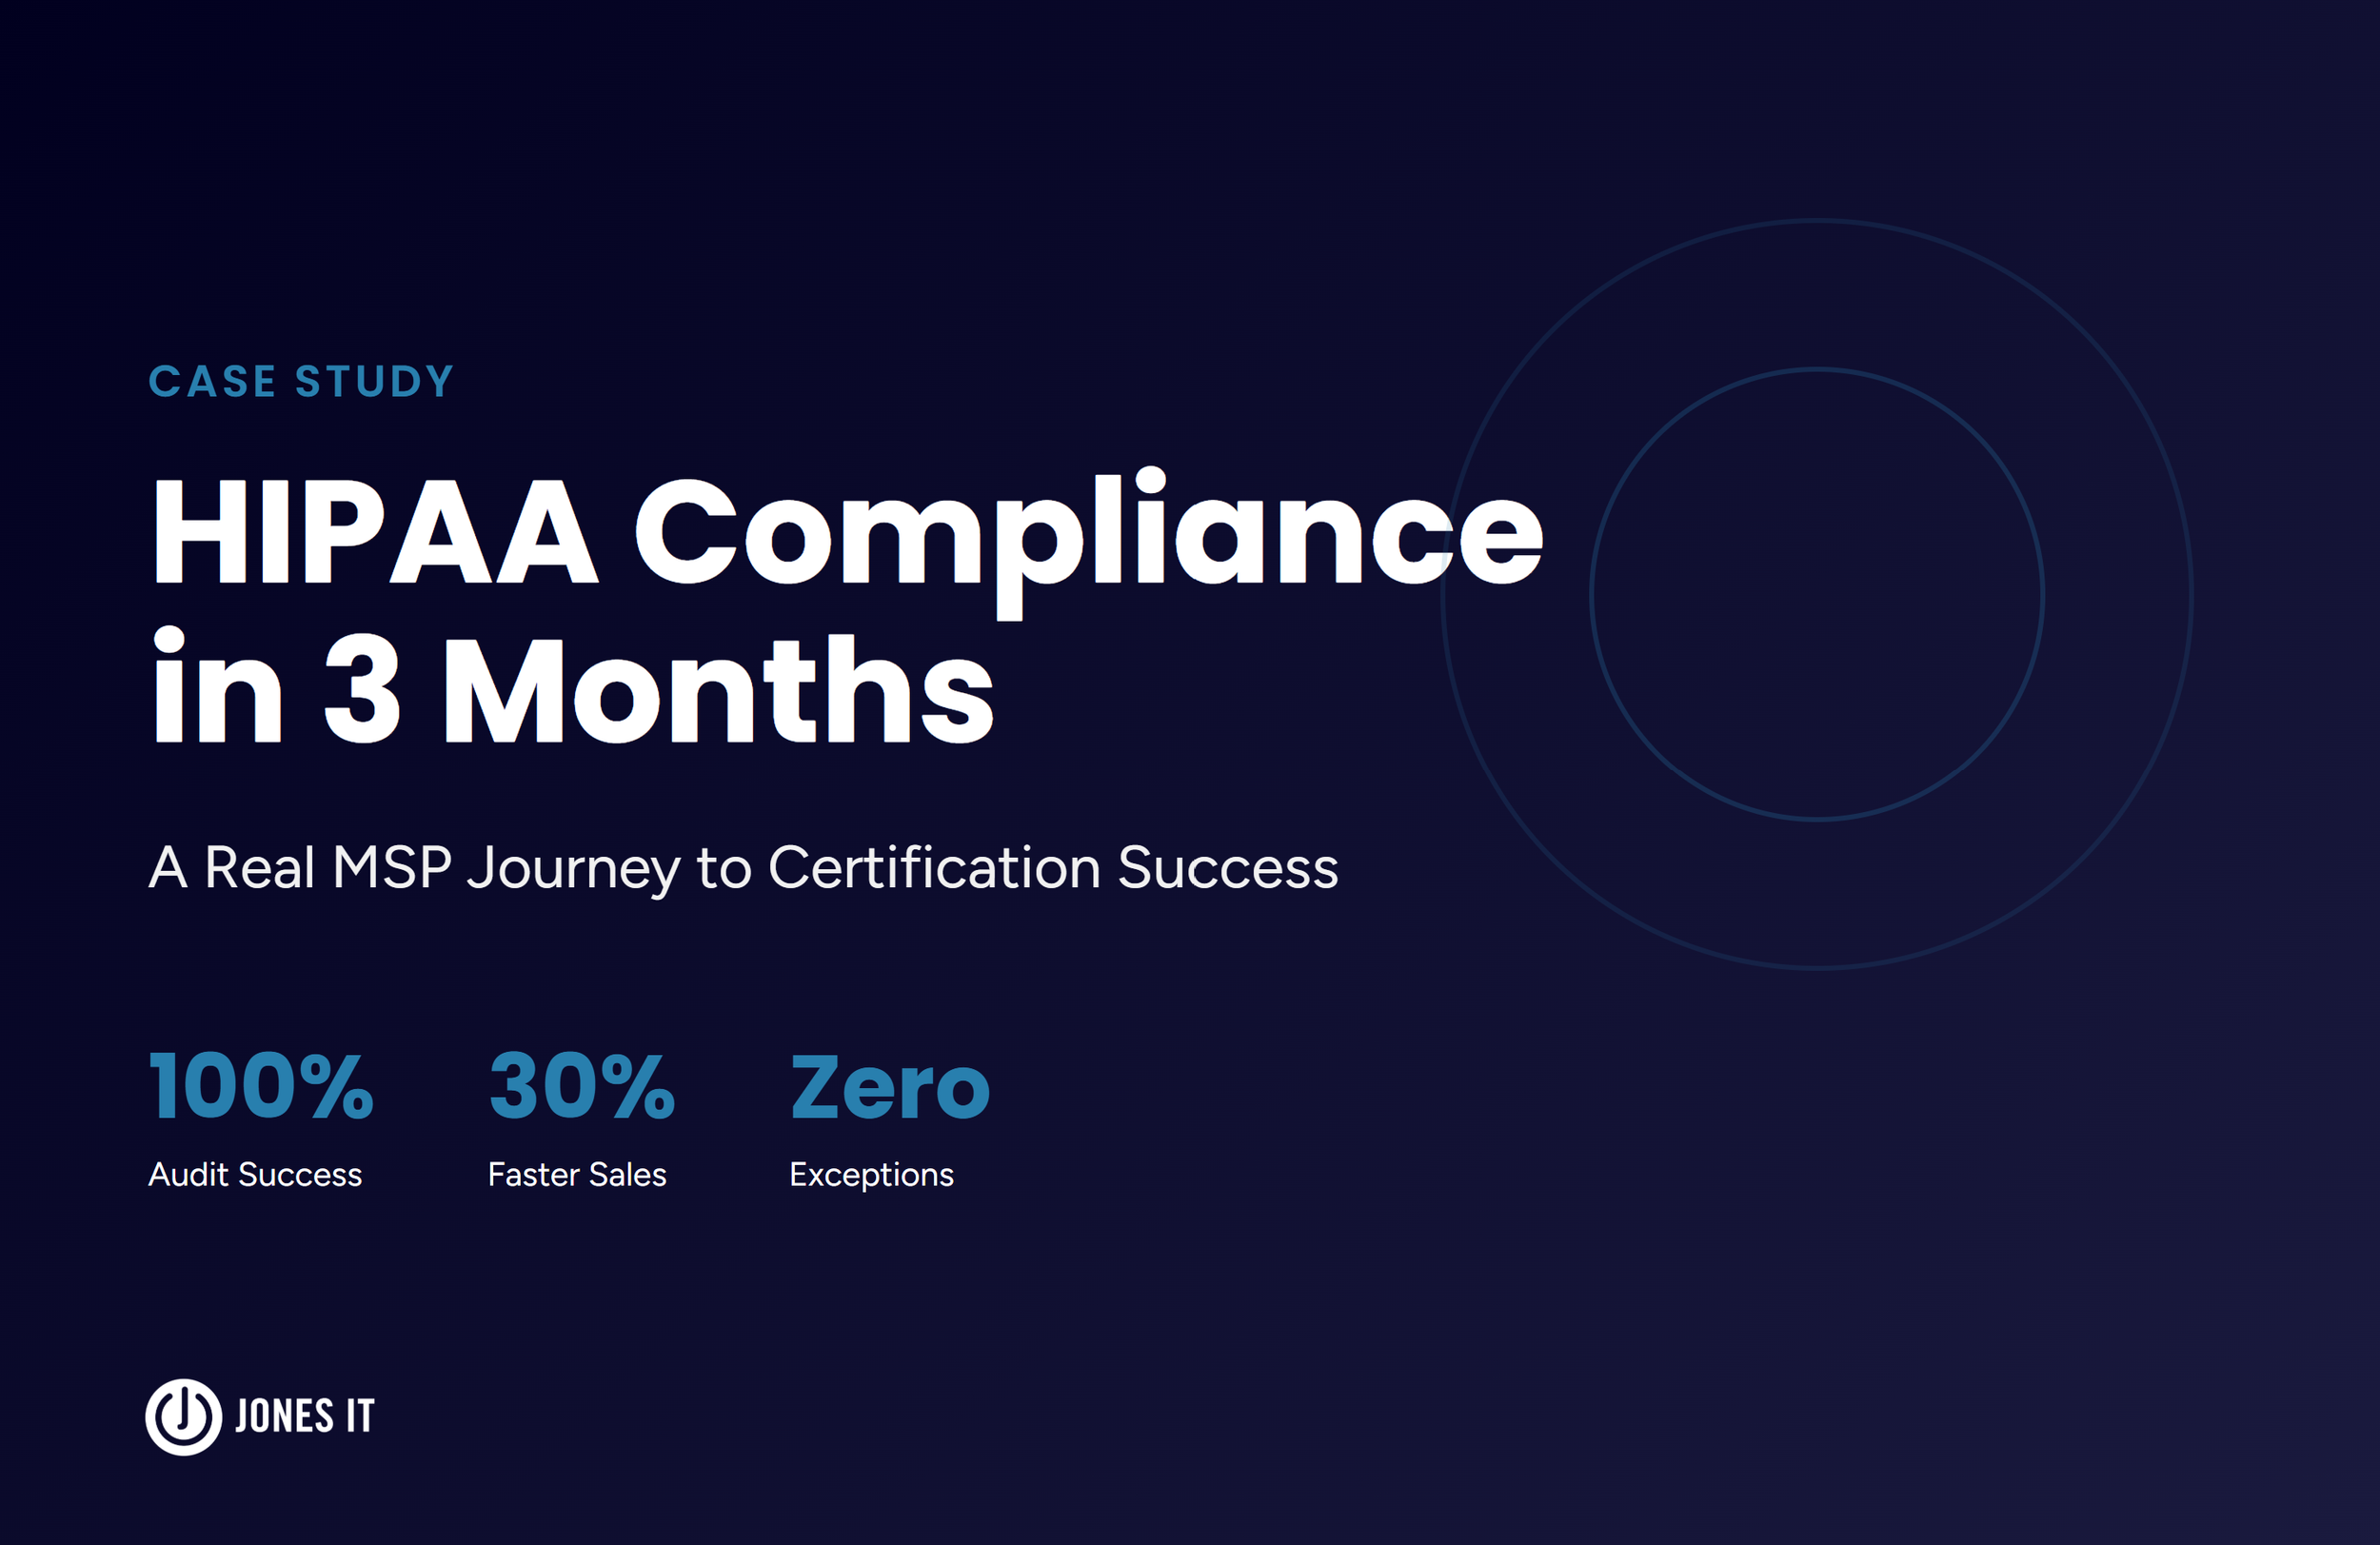
HIPAA Compliance in 3 Months: A Real MSP Case Study
Real story of achieving HIPAA compliance in 90 days using automation and smart strategy. A practical guide to certification, automation, and avoiding costly mistakes.
ISO 27001 in 6 Months: How We Achieved Enterprise-Grade Security Compliance
ISO 27001 in 6 months: Our complete roadmap from SOC 2 to ISO 27001 certification. Tools, timeline, budget insights, and lessons for SME compliance.
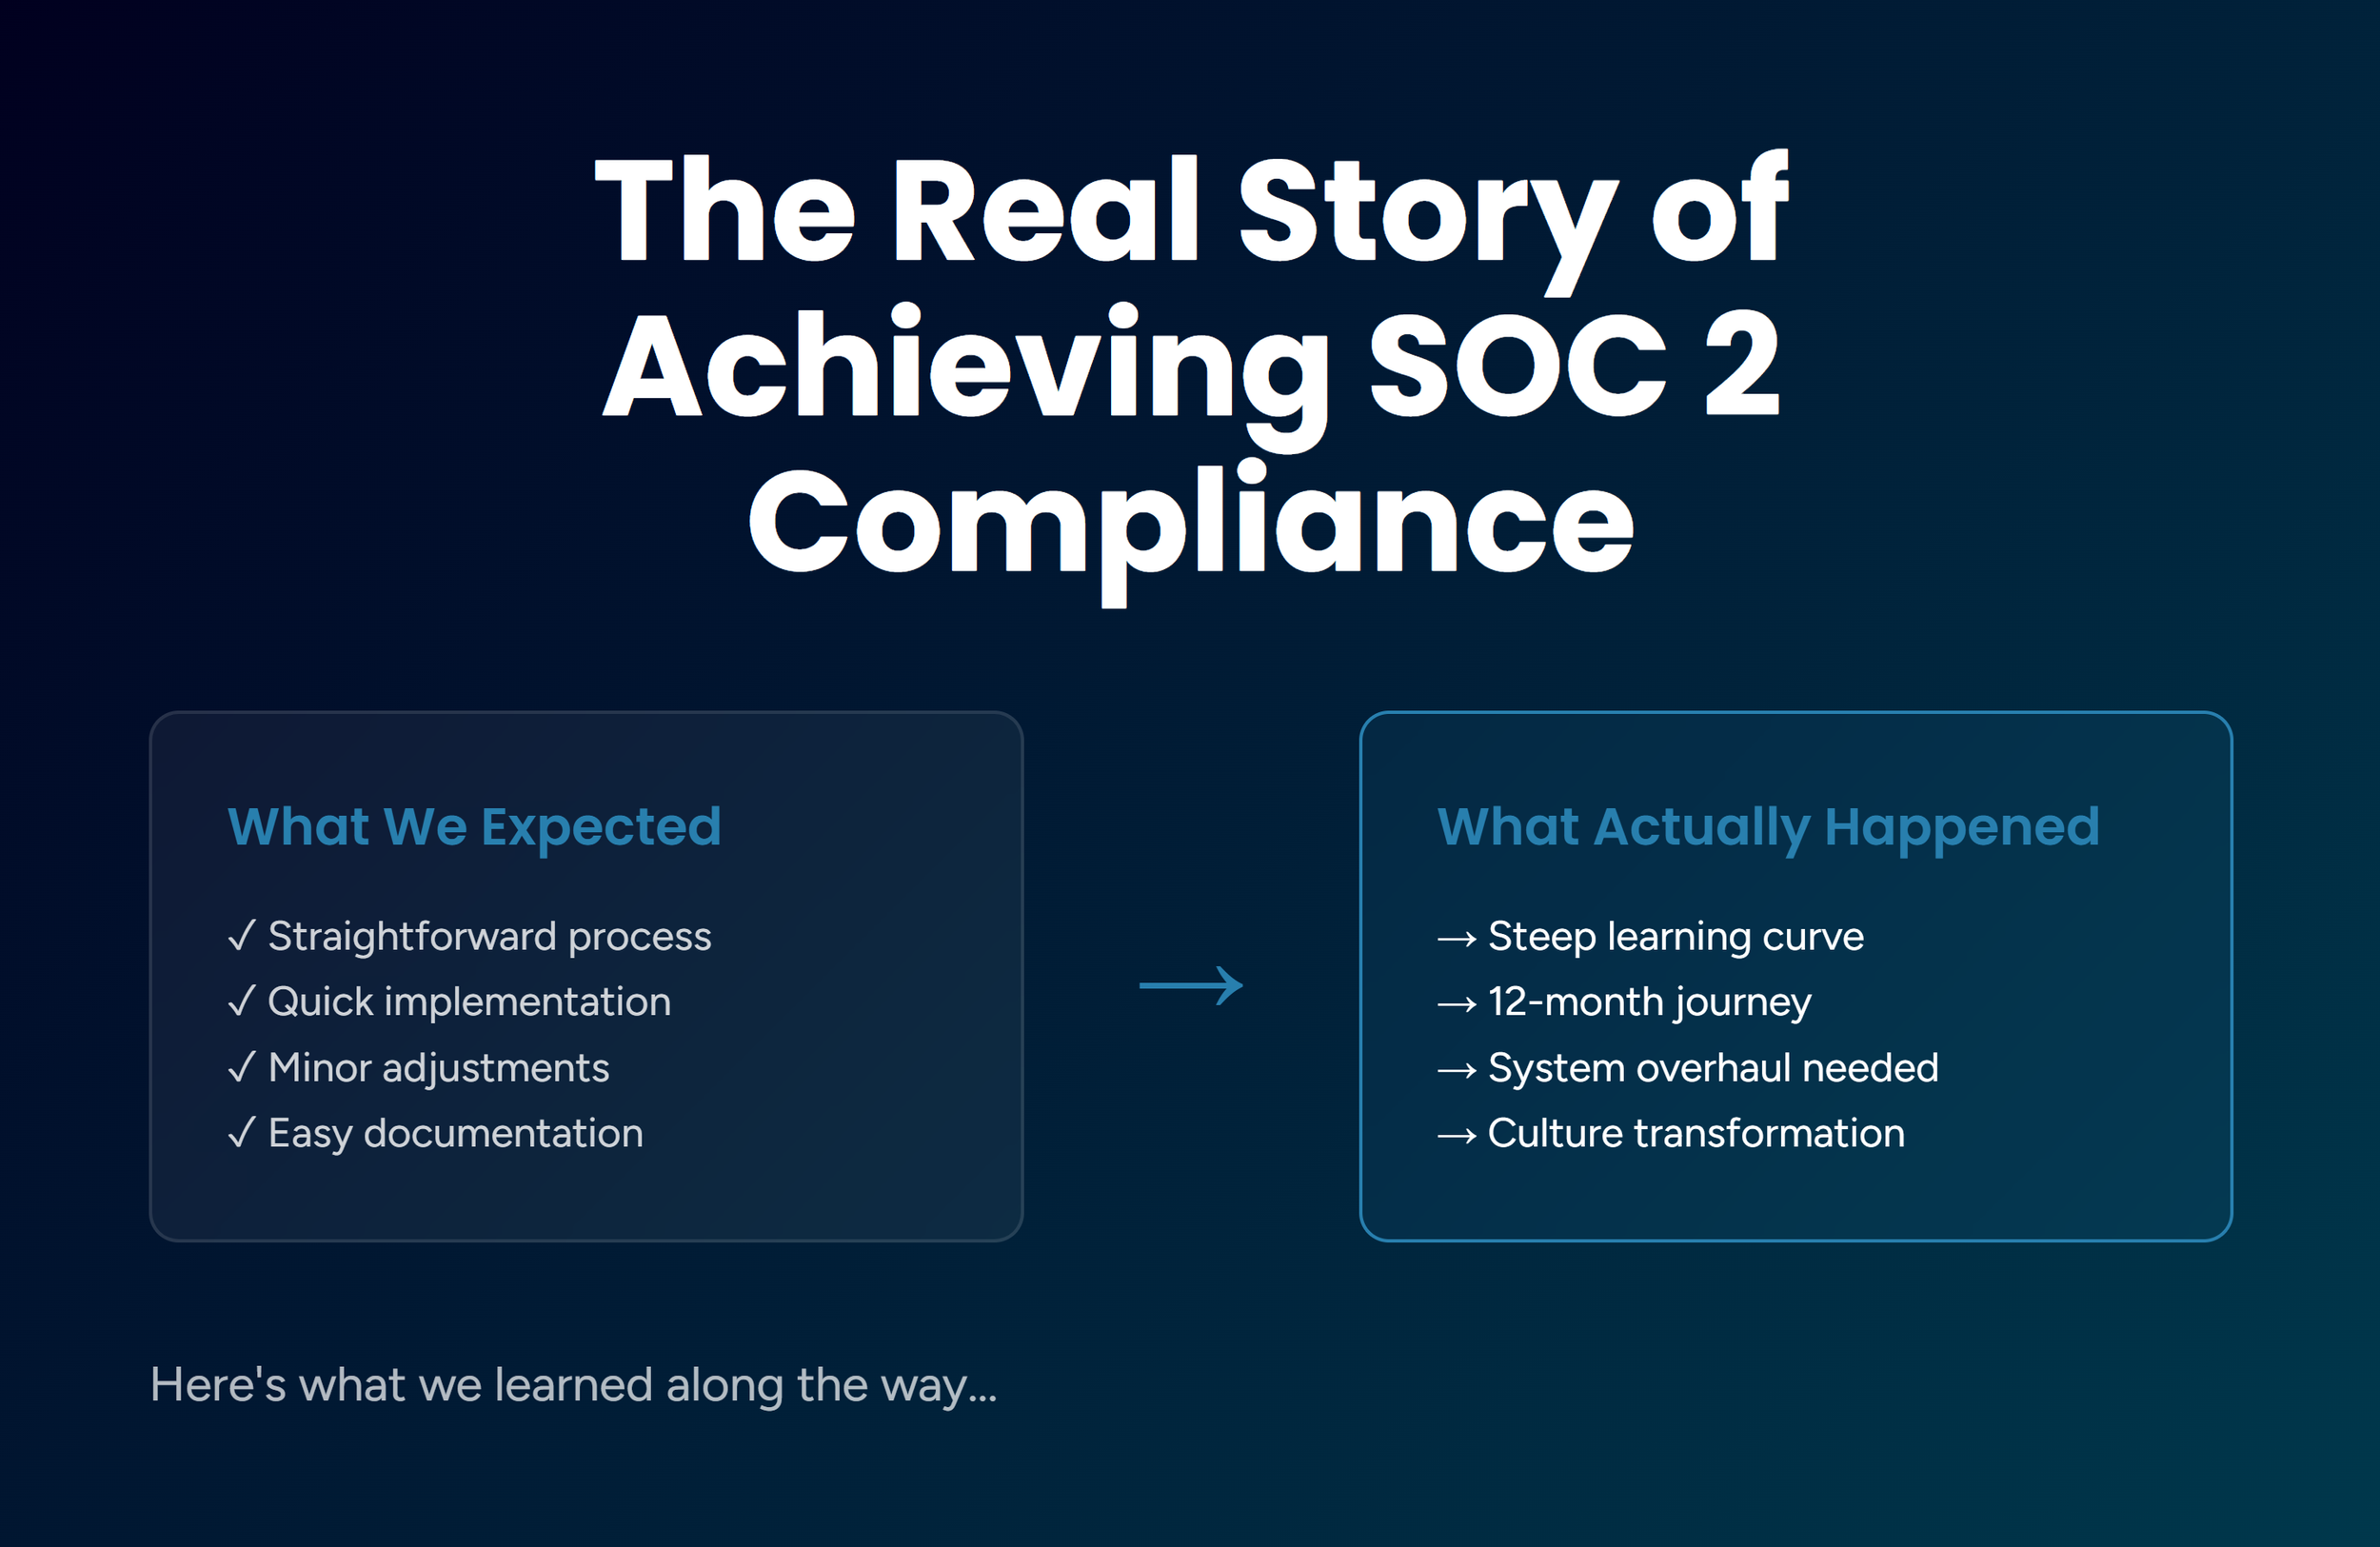
The Real Story of Achieving SOC 2 Compliance: What We'd Do Differently
The real story of achieving SOC 2 Type 2 compliance: 4 major obstacles, tools that worked, and 5 lessons that could save your startup months of effort.
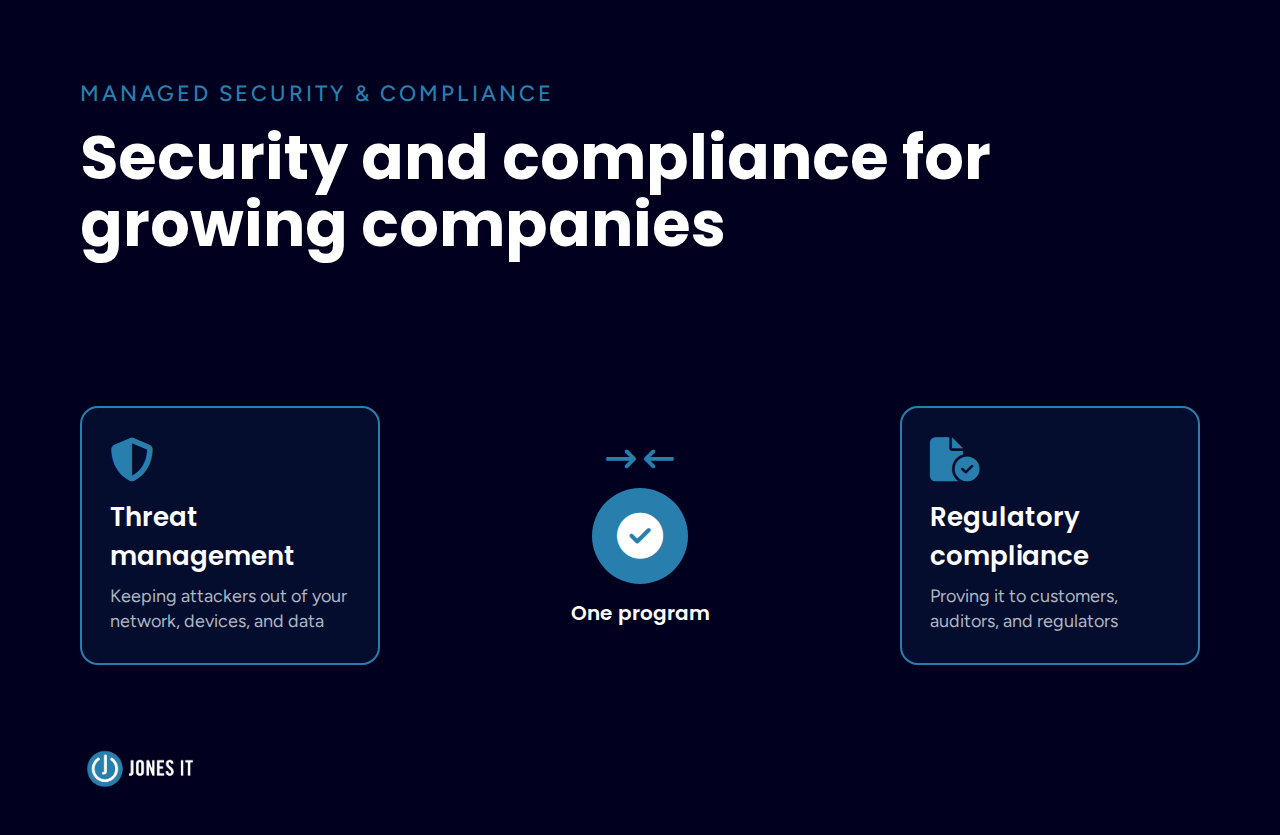
How Jones IT Ensures Security and Compliance for Our Clients
Here’s how managed security and compliance services for growing companies help them meet SOC 2, HIPAA, and PCI DSS requirements, and prevent security breaches.
Schedule a Call with our experts
Get a free consultation and see how Jones IT can tailor solutions to your specific business needs.